For an overview of Git integration options (auth types, Cloud vs Satellite), see Git Integration.
- github.com via the Resolve-managed app, fastest path. One-click install, no app credentials to manage. See Connect via the Resolve-managed app.
- Bring-your-own GitHub App, for GitHub Enterprise Server (on-prem), GitHub Enterprise Cloud, or github.com when you want to operate the app yourself. See Bring Your Own GitHub App.
- Token auth, fine-grained or classic PAT for any GitHub variant; useful for mixed-provider setups. See Git Integration for token-auth setup.
How it works
ResolveAI integrates with GitHub through a GitHub App. Once installed:- GitHub automatically issues a short-lived installation token per request. You never manage or rotate personal access tokens. ResolveAI handles token lifecycle and refresh behind the scenes.
- The agent pulls in relevant code, commits, and pull requests as part of an investigation to help you quickly zero in on the root cause.
- You can ask questions that span your telemetry and your codebase, and ResolveAI connects the dots for you.
- When you ask for a fix, Resolve proposes code changes and opens a pull request for your review. It never pushes commits or merges on its own, remediation is always a user-invoked, review-first flow. This is why the app needs write access on code and pull requests (see Step 3).
- Resolve can trigger GitHub Actions workflows, dispatching, retrying, or cancelling runs so an investigation can carry through to a deployment or a rollback. This is an opt-in feature, currently in Preview, contact help@resolve.ai if you want it enabled.
Connect via the Resolve-managed app
Use this on github.com when you can install the Resolve-managed GitHub App. It’s the fastest path, no app credentials, no private key, no base URL.Prerequisite: log in to your ResolveAI account first, then go to the Integrations page.
- Log in to the ResolveAI App at app0.resolve.ai
- Open the Git Integration page
- Create a new integration, add a Name and click Install Application
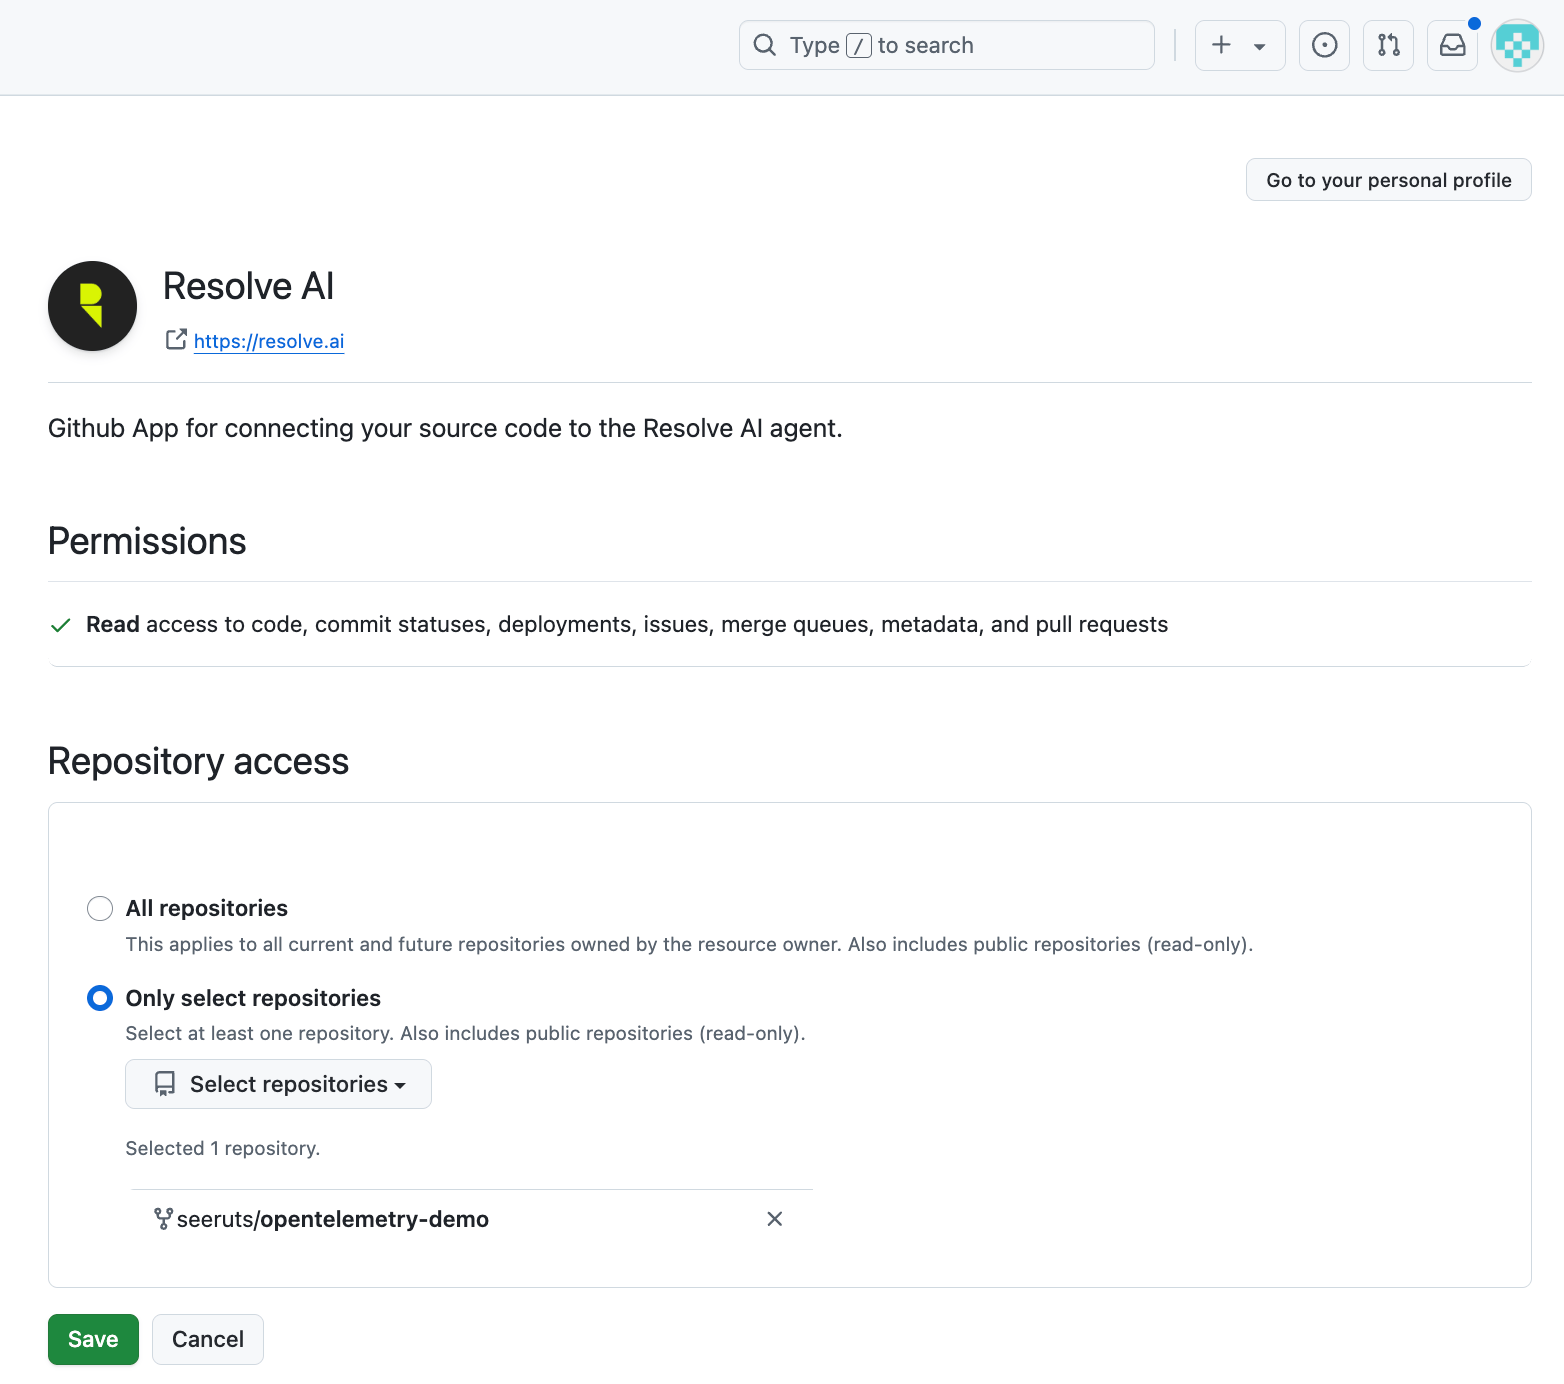
- In GitHub, pick all or a subset of your repositories in the dropdown and click Save
Bring Your Own GitHub App
Create a GitHub App you own, install it on your organization, and connect it to Resolve via the Git integration’sghe auth type.
The same procedure works for all GitHub variants:
- github.com, when you’d rather operate the app yourself instead of installing the Resolve-managed one (compliance, audit, scoped permissions)
- GitHub Enterprise Cloud
- GitHub Enterprise Server (on-prem), including air-gapped instances reachable only from inside your network (use a Satellite)
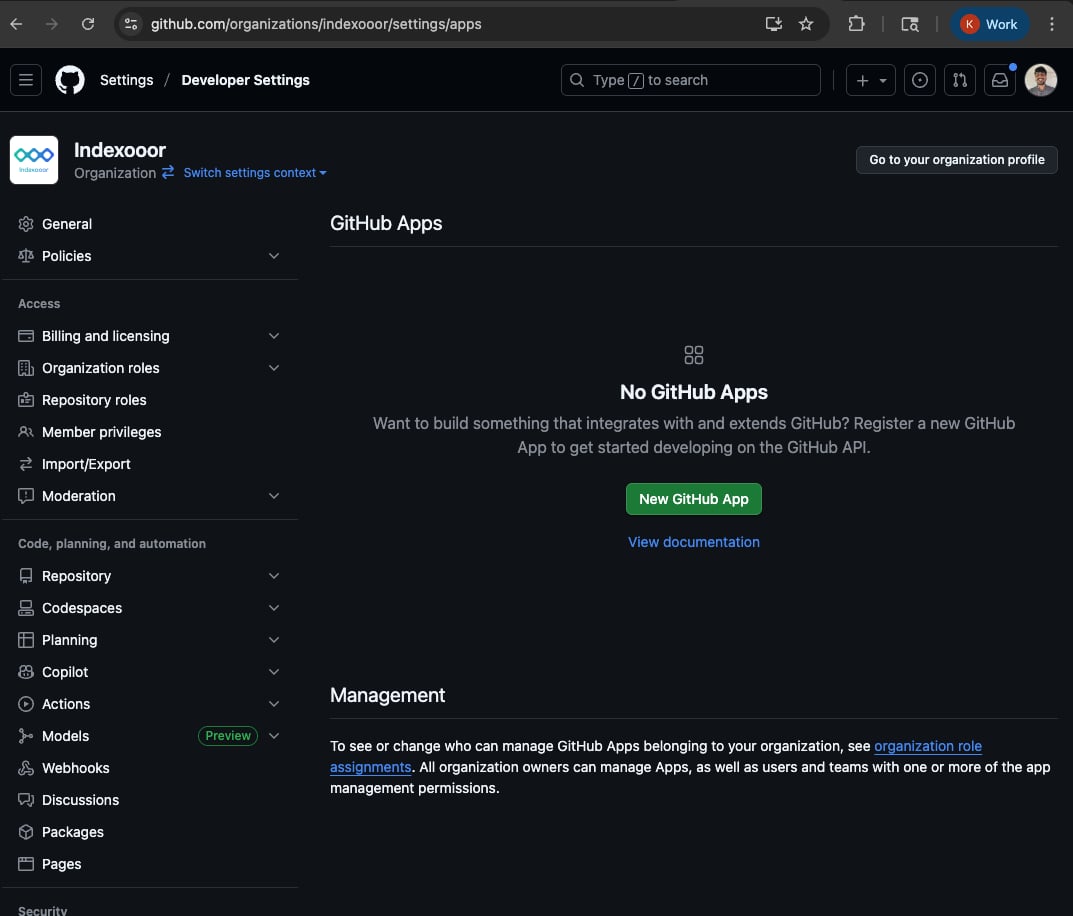
Step 1: Navigate to Developer Settings for the org account
- Log in to your GitHub instance (github.com or your GHE Server URL).
- Navigate to your organization’s main page.
- In the left sidebar, click Settings.
- Click Developer settings > GitHub Apps.
Step 2: Click on New GitHub App
Click New GitHub App and fill in the basic details:- GitHub App name: e.g.
ResolveAI(must be unique on the instance) - Homepage URL:
https://resolve.ai/ - Webhook: uncheck Active, Resolve does not consume GitHub webhooks
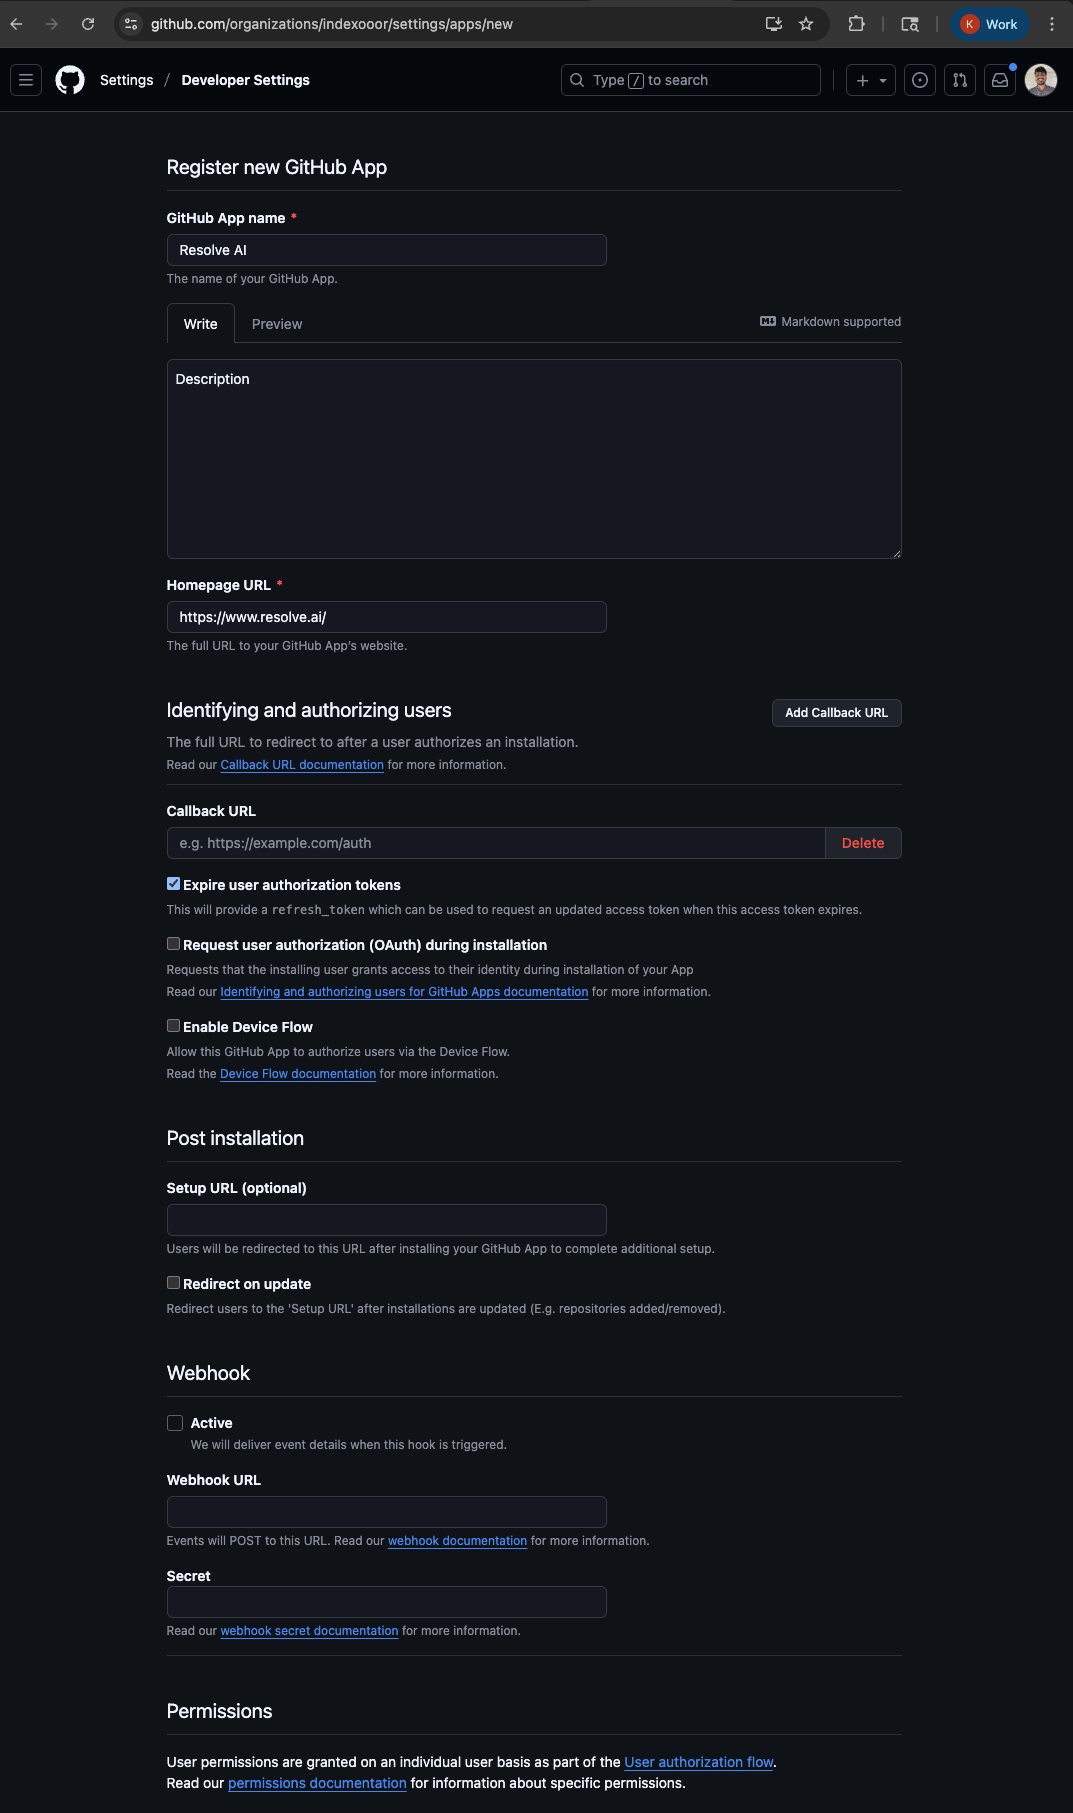
Step 3: Set repository permissions
Grant the GitHub App the following repository permissions:Read access to: checks, commit statuses, deployments, discussions, issues, merge queues, and metadata Read and write access to: code (Contents), pull requests, and actionsThe read scopes let Resolve pull code and investigation context. The read-and-write scopes on code and pull requests let it propose code changes and open pull requests for your review. Read and write on actions backs workflow triggering, which is in Preview and off unless enabled for your organization. To keep specific workflows out of reach, scope the app installation so it excludes those repositories. Repository selection, not the permission level, is the lever here.
Granting only Read on code and pull requests keeps Resolve in investigate-only mode: it cannot open PRs, and remediation fails at runtime.
Updated permission. Actions is now Read and write, which additionally backs workflow triggering. If you installed Resolve’s app before this change, accept the prompt to apply the updated permissions on the existing installation, no reinstall is required.
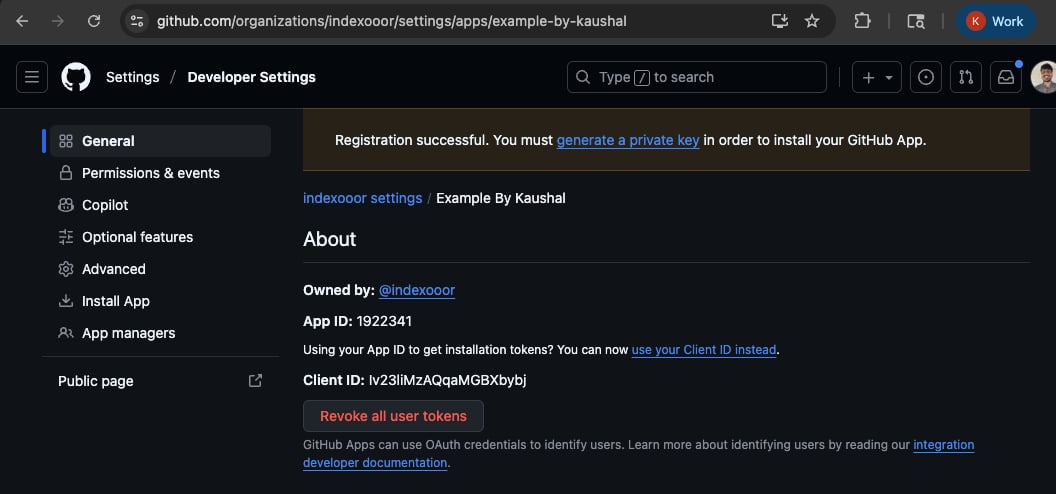
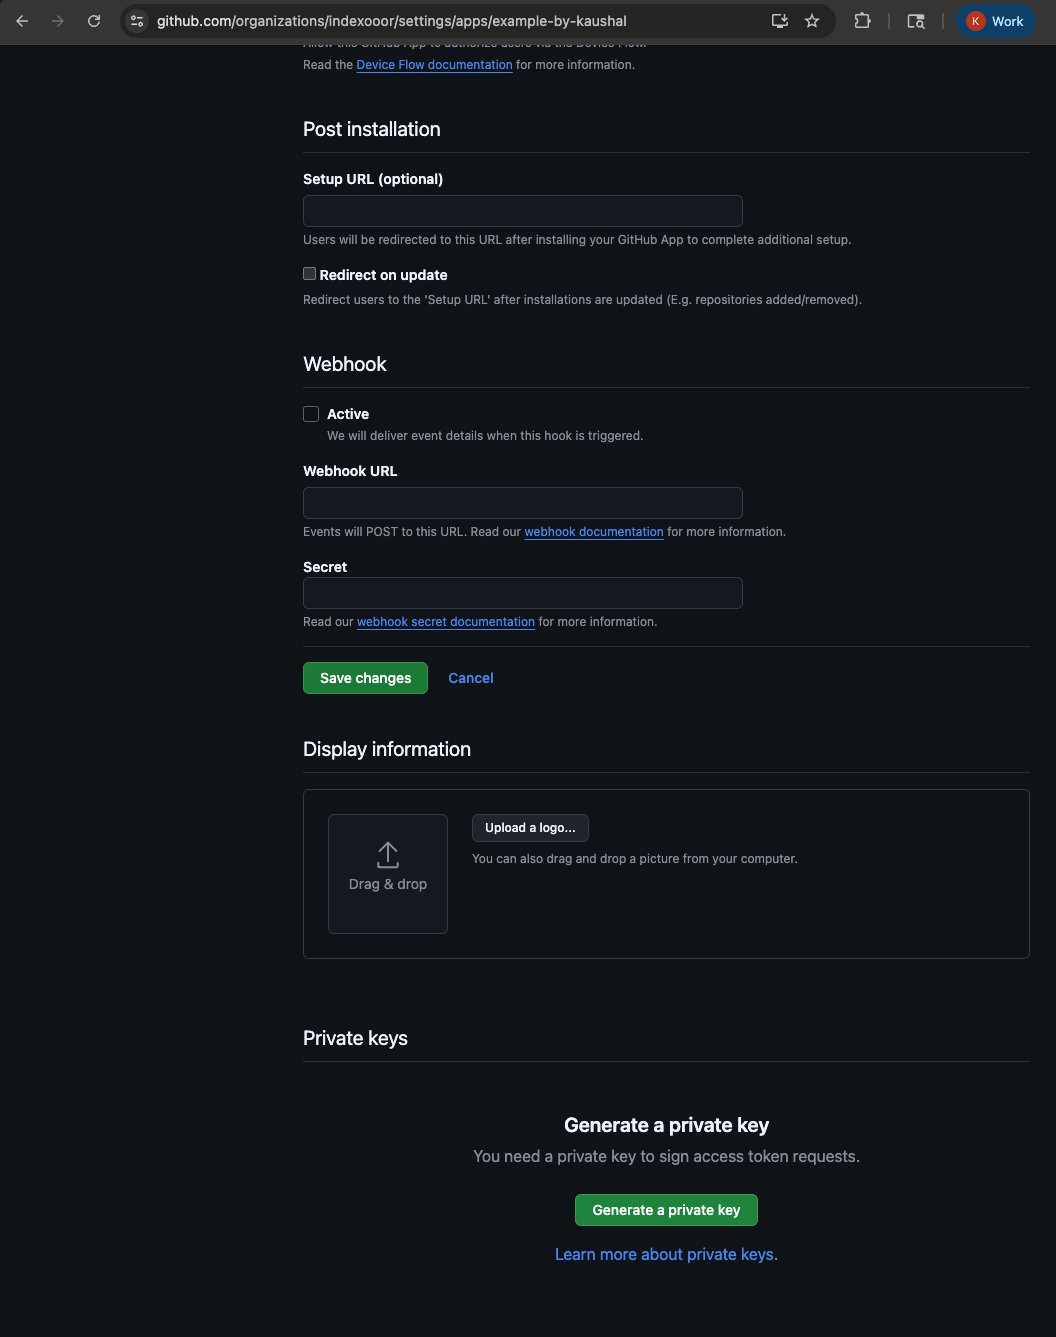
Step 4: Collect credentials and generate a private key
After saving, capture from the app settings page:- App ID, shown on the General tab
- Private key, scroll down to Private keys and click Generate a private key; a
.pemfile downloads. Store it somewhere safe, GitHub will not show it again.
Step 5: Install the GitHub App
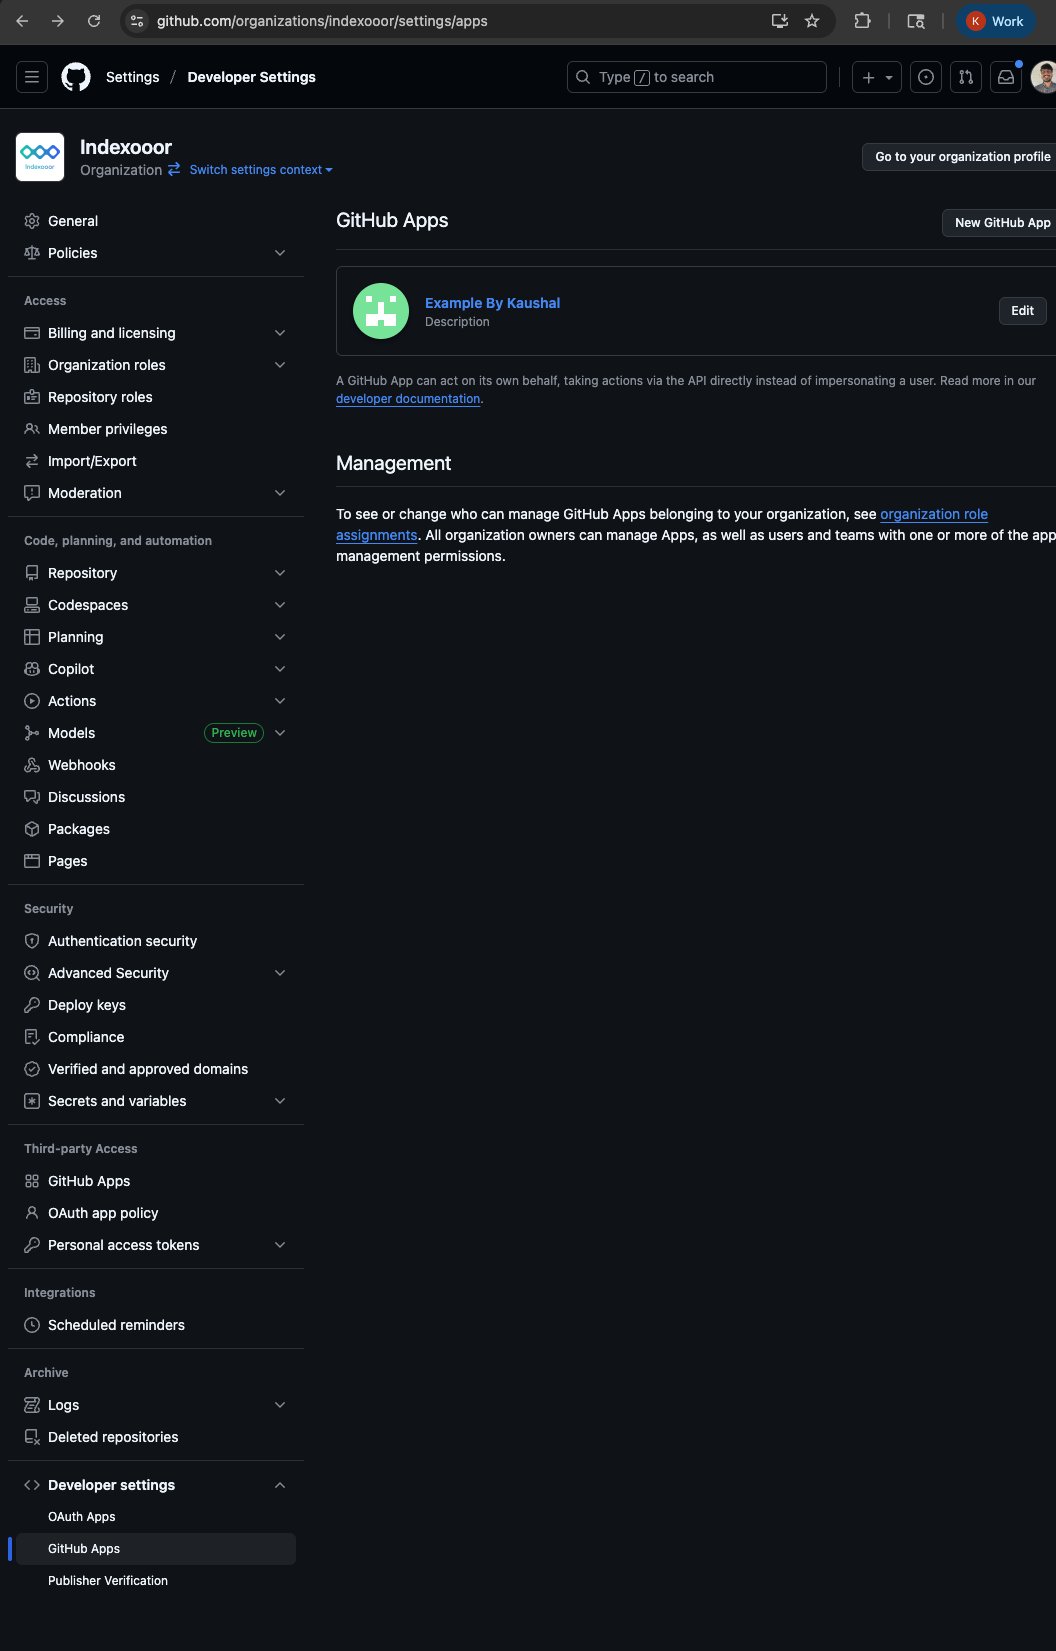
From the app settings page:- Click Edit on the app you just created (or Install App in the left sidebar).
- Click Install next to your organization.
- Choose All repositories or Only select repositories and pick the repos you want Resolve to access.
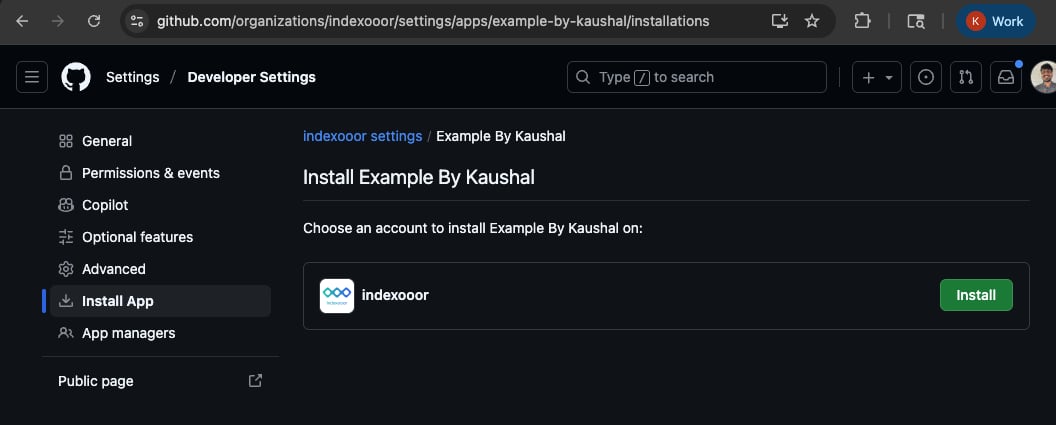
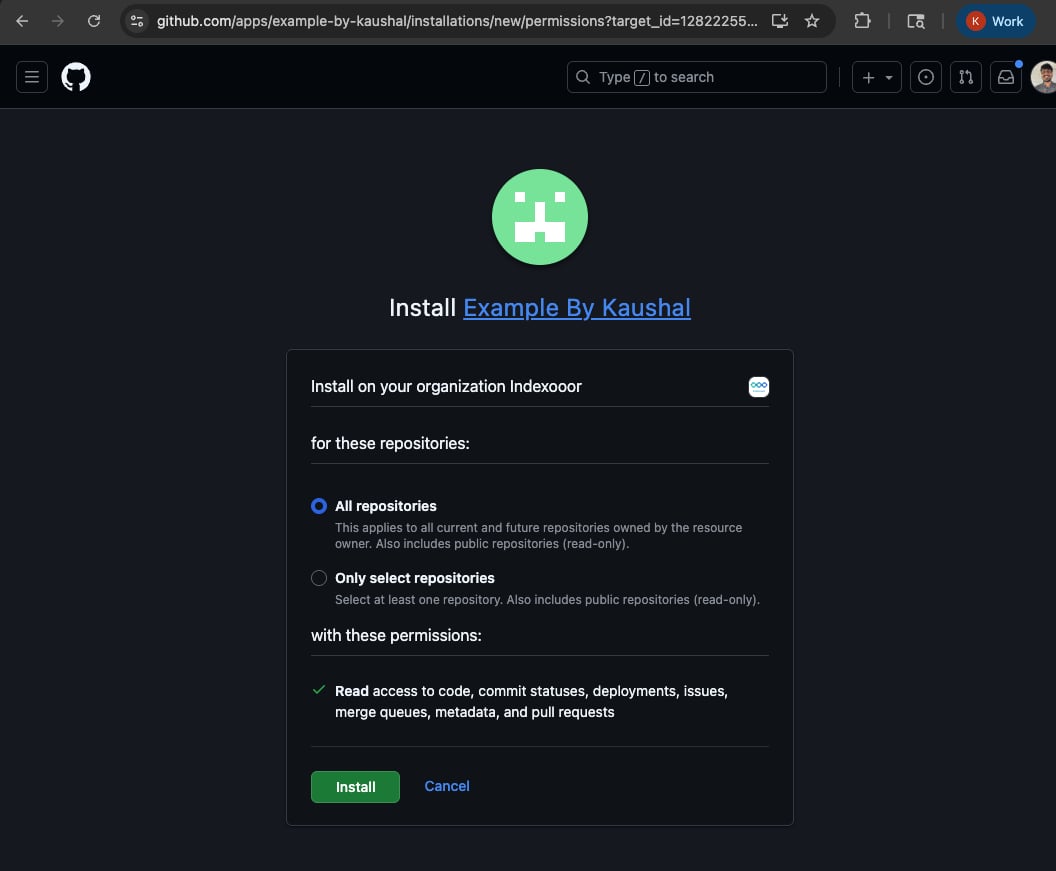
The permission summary GitHub shows on this screen mirrors exactly what you configured in Step 3. Confirm it matches the full recommended set: Read and write on code and pull requests (this is what enables PR creation), Read and write on actions, plus Read on checks, commit statuses, deployments, discussions, issues, merge queues, and metadata. An older install may show a narrower summary, for example read-only on actions. If so, return to the app’s Permissions & events settings, add the missing permissions, and accept the update prompt on the existing installation (no reinstall needed).
Step 6: Collect the Installation ID and base URL
Installation ID
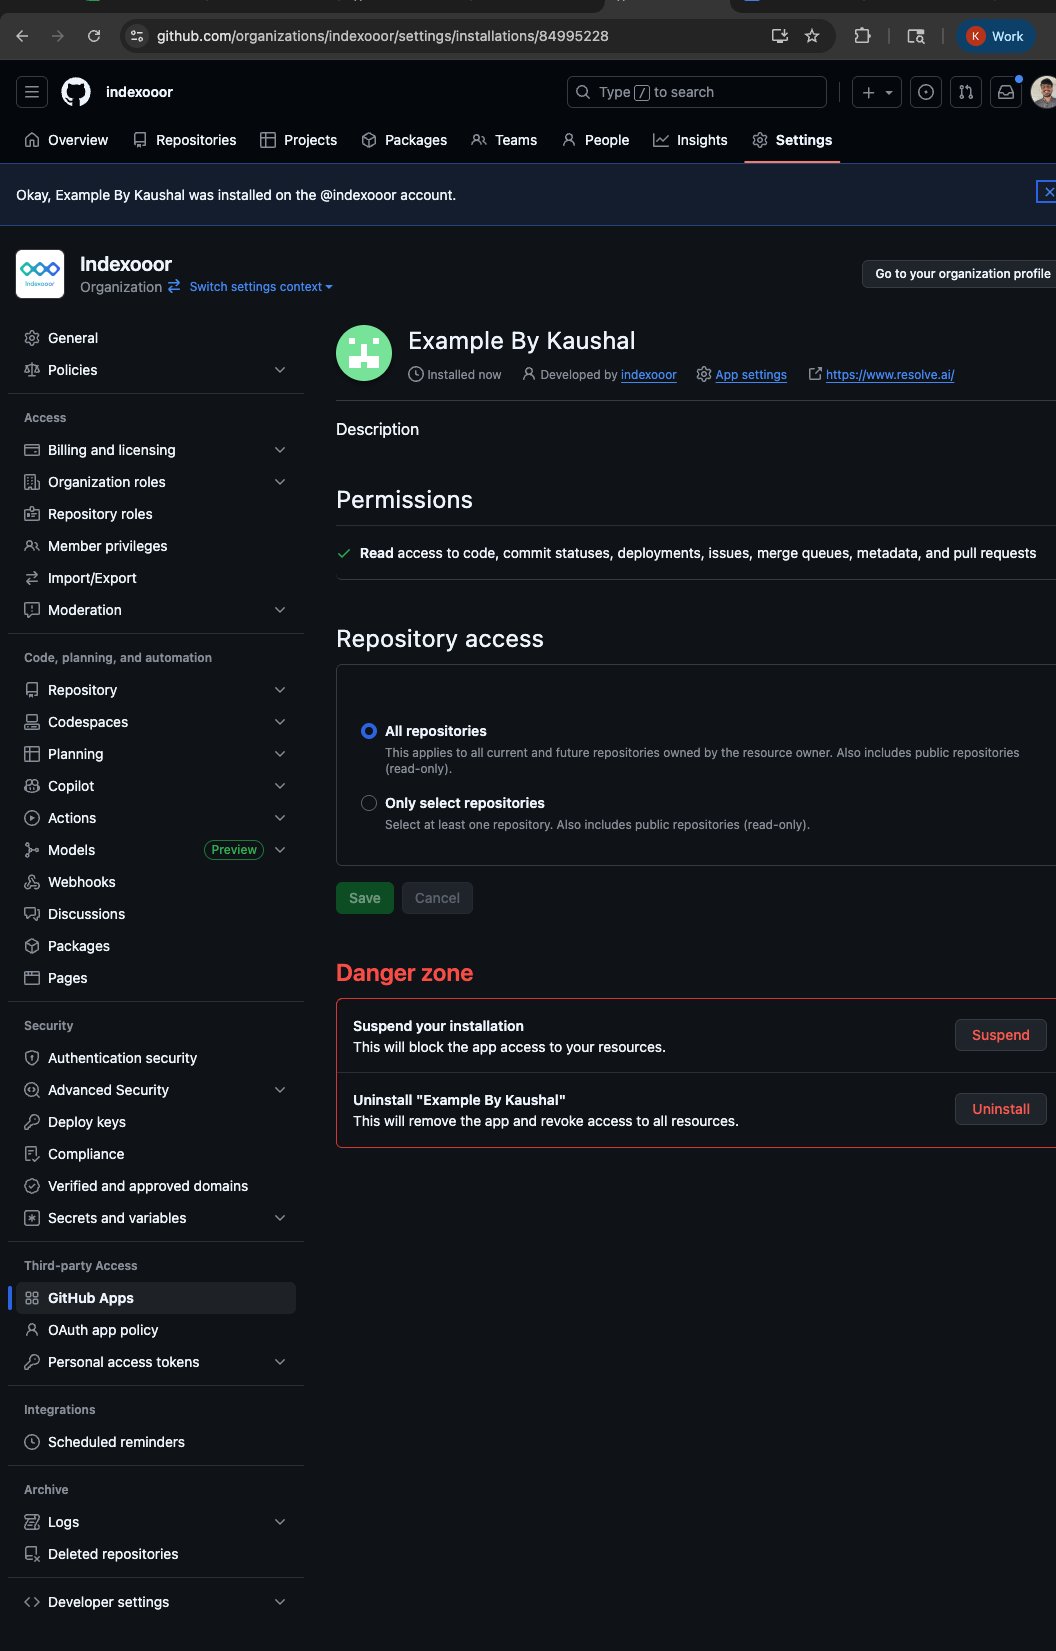
Path: Profile picture > Settings > Applications > Configure (on the app you just created). The installation ID is the trailing number in the URL. Example:https://github.com/organizations/<your-org>/settings/installations/84995228, installation ID is 84995228.
API base URL
For older GHE Server versions or custom-overridden base URLs, contact your GitHub administrator.
Step 7: Configure the Resolve integration
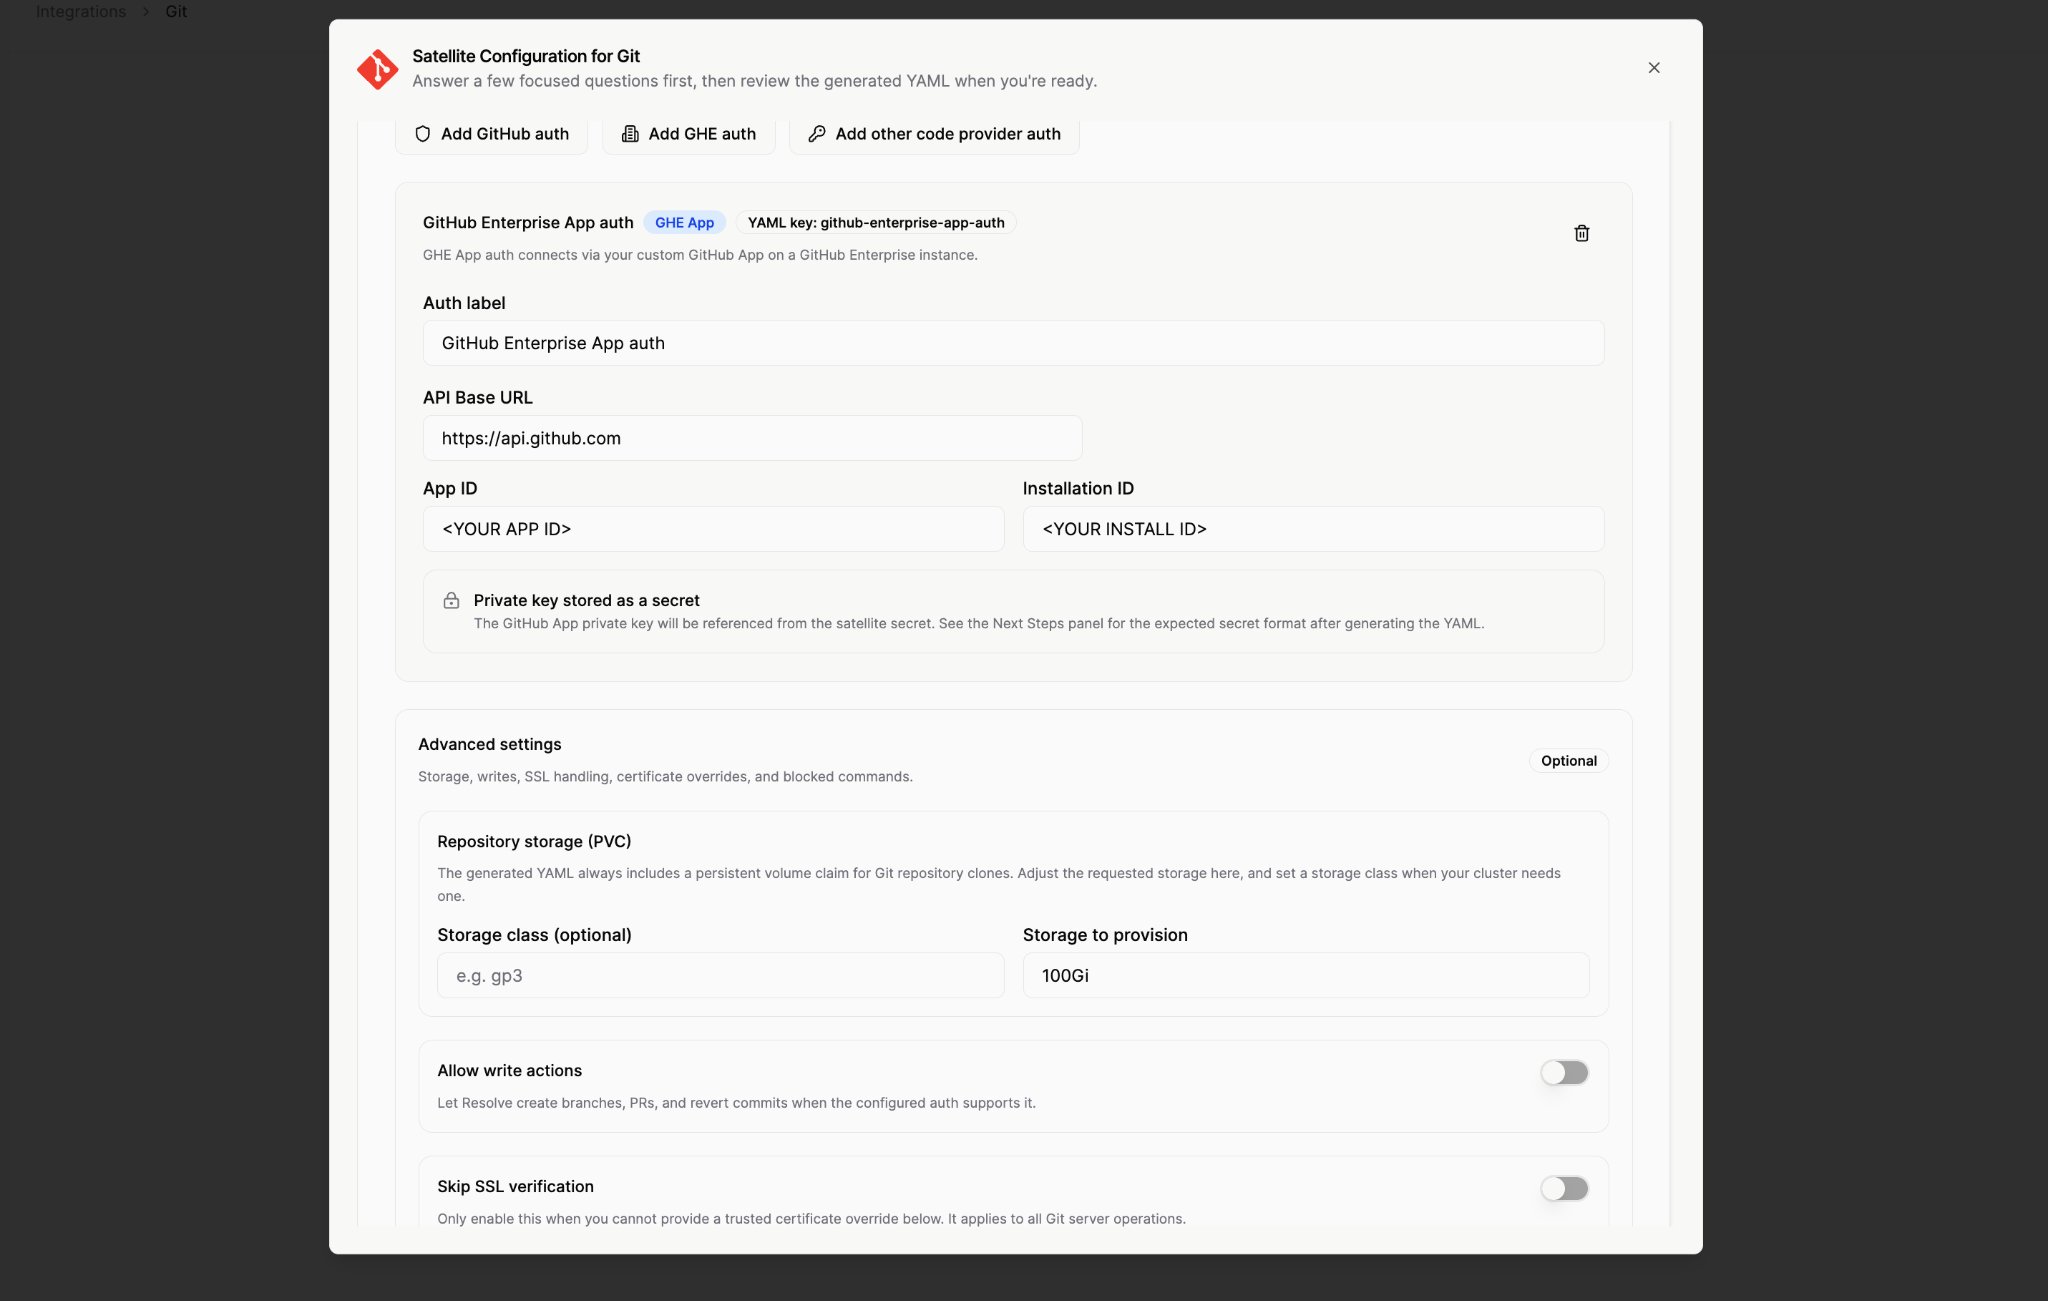
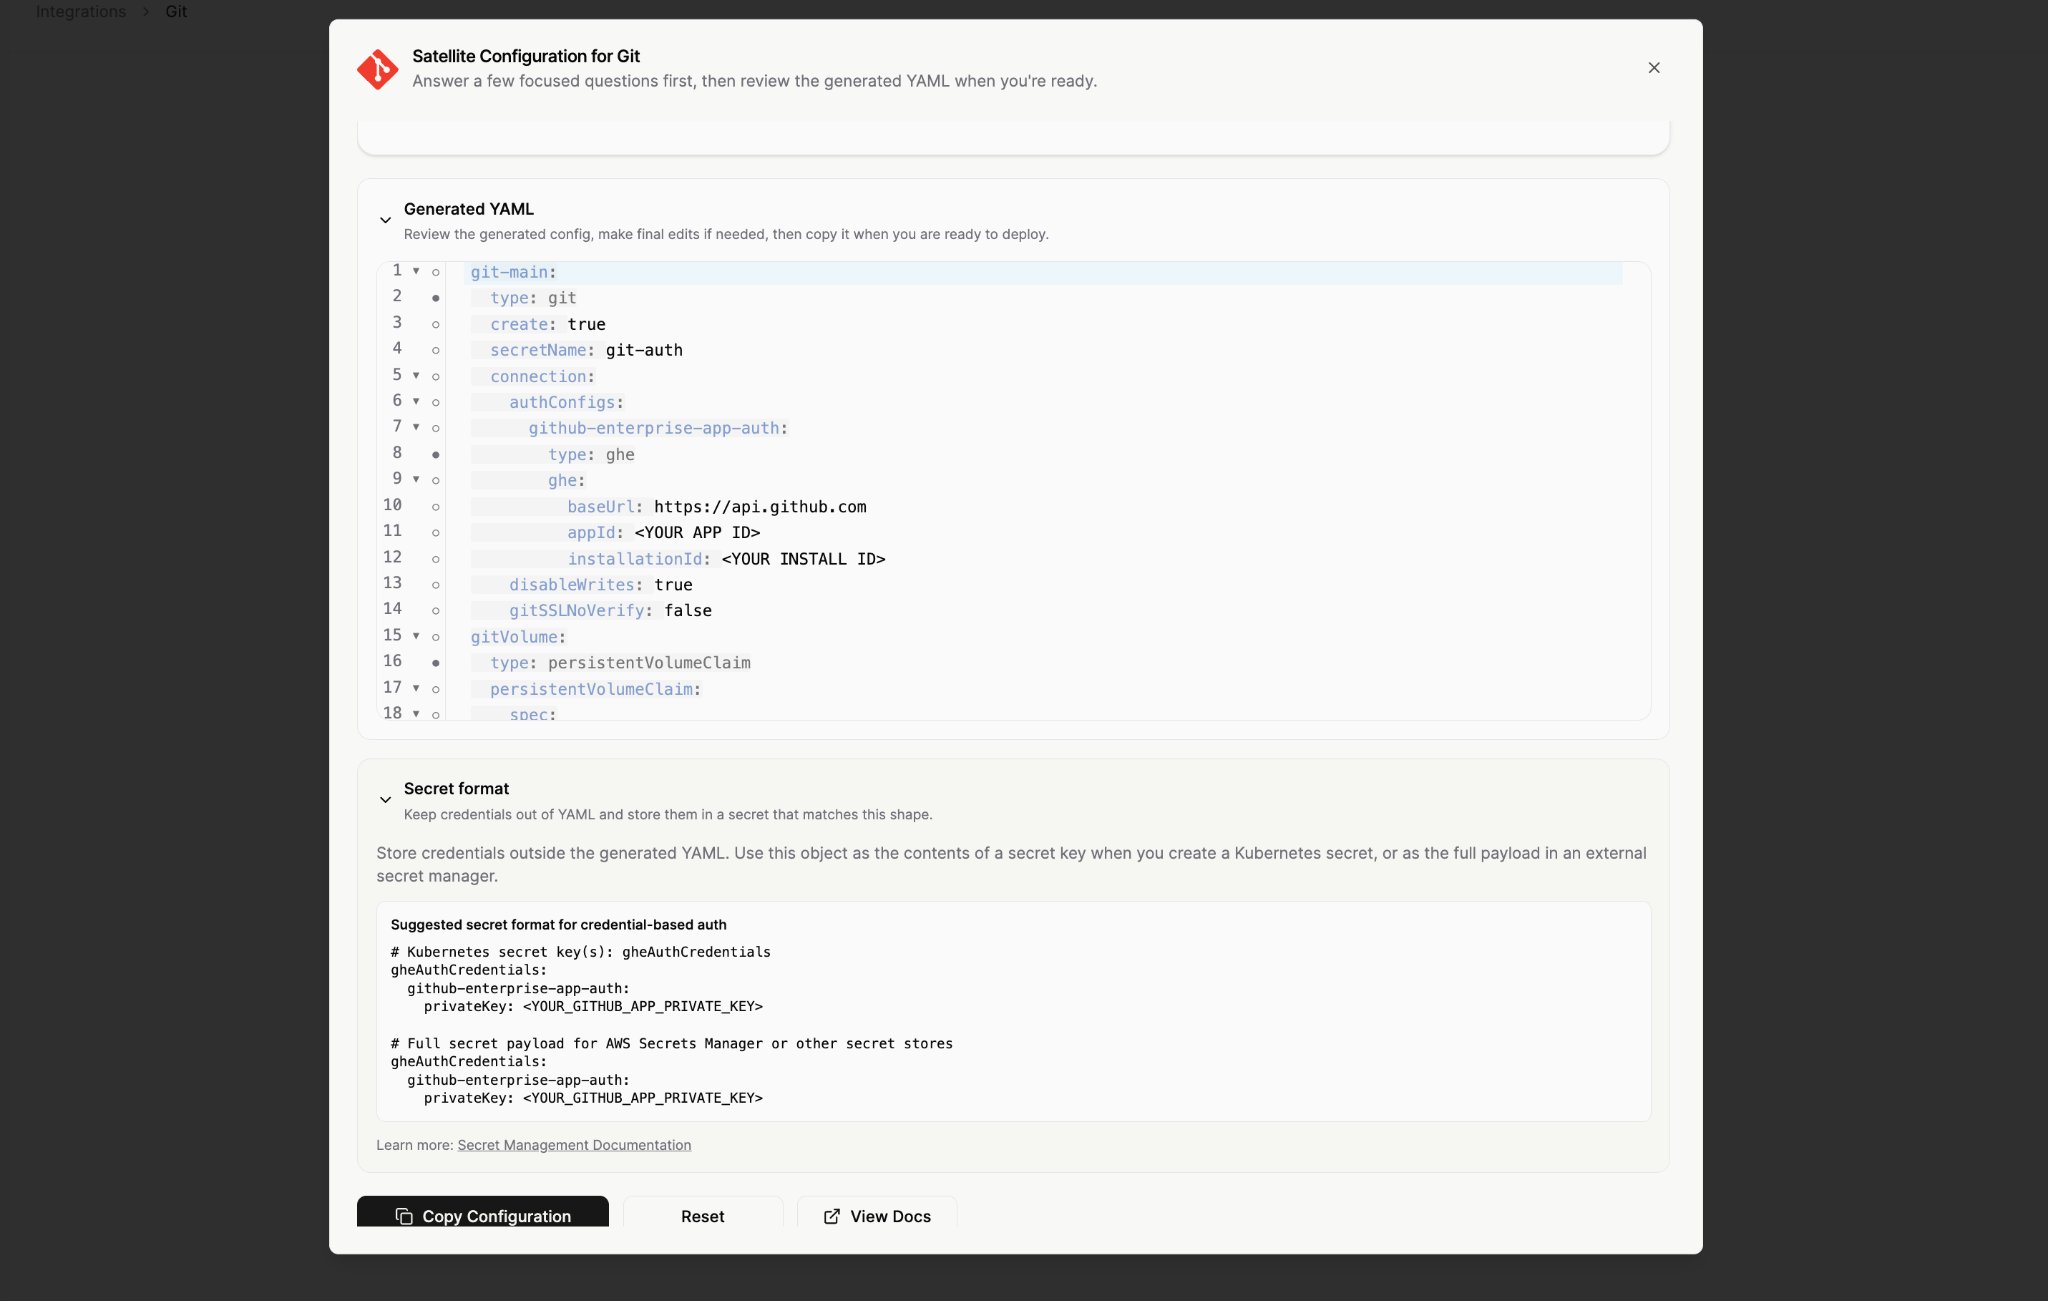
Connect the BYO app to Resolve through the Git integration’sghe auth type. Pick SaaS if your GitHub instance is reachable from the public internet, or Satellite if it lives inside your network.
- SaaS
- Satellite
Connect via Resolve UI (Cloud)
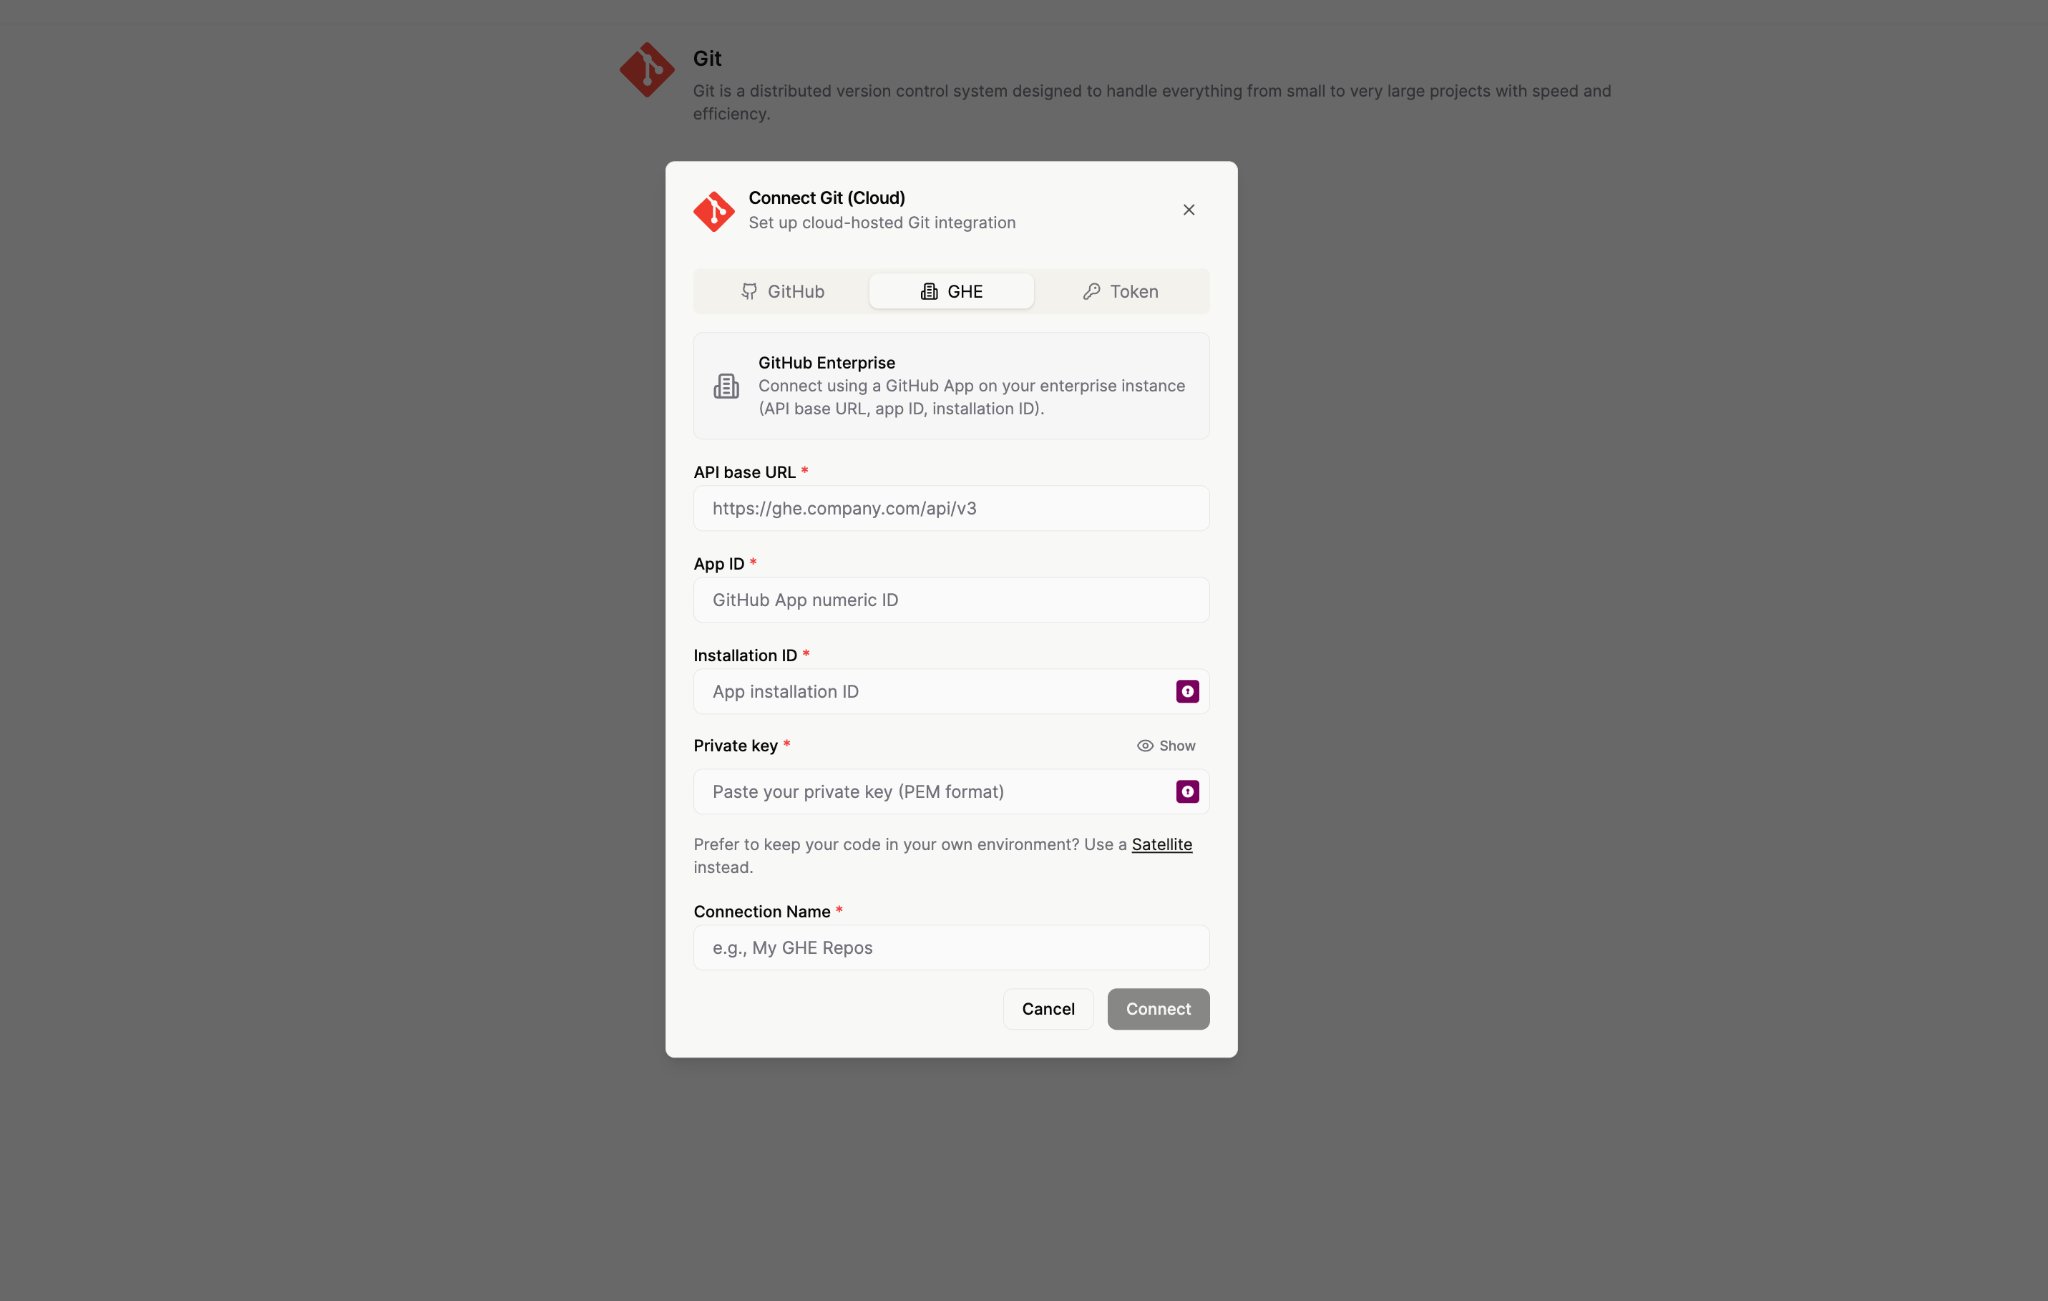
- Open Git Integrations.
- Create a Cloud Git connection.
- Select the GHE auth tab.
- Fill in the four fields:
-
Save and verify the health check and repository listing.
GitHub App permissions reference
GitHub App permissions reference
Capabilities only become available when the matching permission is granted on the app installation.
If a feature returns
403/permission denied at runtime, the app installation is usually missing one of these. Update the app’s permissions on GitHub, accept the prompt to apply the new permission set on the existing installation, then retry.Frequently Asked Questions
How does ResolveAI's GitHub integration work?
How does ResolveAI's GitHub integration work?
The integration is installed as a GitHub App.
- You install the app on any repository you want ResolveAI to read.
- GitHub issues a short-lived installation access token automatically for each request, so you never manage or rotate PATs yourself.
- All token lifecycle and refresh logic is handled by ResolveAI behind the scenes.
What data does it look at?
What data does it look at?
The GitHub App requests the permissions documented in Step 3. With those scopes, during an investigation the agent reads:
- Repository tree (file paths and file contents)
- Pull / Merge Requests (open and merged), including diffs and review comments
- Commit metadata and diffs
- Basic repository metadata (default branch, topics, permissions)
- GitHub Actions workflow definitions and recent runs (statuses, conclusions, head SHAs)
- Check runs and CI status for PRs
- Issues and Discussions referenced as context
Does ResolveAI store the source code?
Does ResolveAI store the source code?
No. Source code is streamed from GitHub at runtime only and is not persisted or mirrored on ResolveAI’s servers. The sole exception is small code snippets that appear in your investigations, which are saved in ResolveAI SaaS or sent to Slack.
Can ResolveAI make changes to my repositories?
Can ResolveAI make changes to my repositories?
The GitHub App has write permissions on Contents (code) and Pull requests, but those are only used for explicit, user-invoked actions. Resolve never auto-pushes commits or opens PRs in the background. The app cannot merge code or alter repository settings.The app also carries Actions (Read & write), which lets Resolve dispatch, retry, and cancel workflow runs. That capability is in Preview and off unless enabled for your organization, and the tools default to requiring human approval.If you want to disable writes entirely on a Git integration, set
disableWrites: true on the integration’s connection. Read-only operations stay available, write/remediation paths are blocked.For BYO setups, you control the granted permissions on your own GitHub App.Can Resolve deploy or roll back without me asking?
Can Resolve deploy or roll back without me asking?
Not by default. The app installation carries Actions (Read & write), but the permission alone changes nothing: every write tool ships on Approval, so out of the box Resolve proposes the deploy or rollback and waits for a person.Set a tool to Auto and that checkpoint is gone for that tool. The effective mode shown next to each tool in Resolve’s settings is the authoritative answer for your org.
How is workflow triggering enabled and controlled?
How is workflow triggering enabled and controlled?
This feature is currently in Preview. Contact help@resolve.ai to have it enabled for your organization. If it is enabled, you can disable specific write tools in your admin settings, and every write tool requires human approval by default.
How do I turn workflow triggering off?
How do I turn workflow triggering off?
Three options, depending on how firmly you want it off:
- Disable the specific tools in your admin settings, or leave them on Approval so nothing runs without a person approving it.
- Remove the repositories from the app installation, which puts their workflows out of reach entirely. Use this when only some repositories should be off limits.
- Ask us to disable the Preview for your organization, at help@resolve.ai. On a bring-your-own app you can also set Actions back to Read-only yourself, or narrow the fine-grained PAT for token auth. Investigations keep working either way, they retain read access to workflow runs and definitions.
Whose identity do write actions run under?
Whose identity do write actions run under?
That depends on the tool’s credentials setting.
- Shared credentials (the default) run the action with the Git integration’s own credentials. In GitHub’s audit log the actor is the app installation, not the person who approved.
- Per-user auth runs the action under the individual user’s own GitHub authorization. The action then appears in GitHub’s audit log as that person, and it is bounded by their repository permissions, so a user cannot use Resolve to do something GitHub would not let them do directly.
I'm using a GitHub IP allowlist. How do I connect with Resolve?
I'm using a GitHub IP allowlist. How do I connect with Resolve?
GitHub IP allowlistContact us at help@resolve.ai to manage the allowlist of IP addresses for ResolveAI to connect to your GitHub organization.