How Resolve connects to your codebase through Git
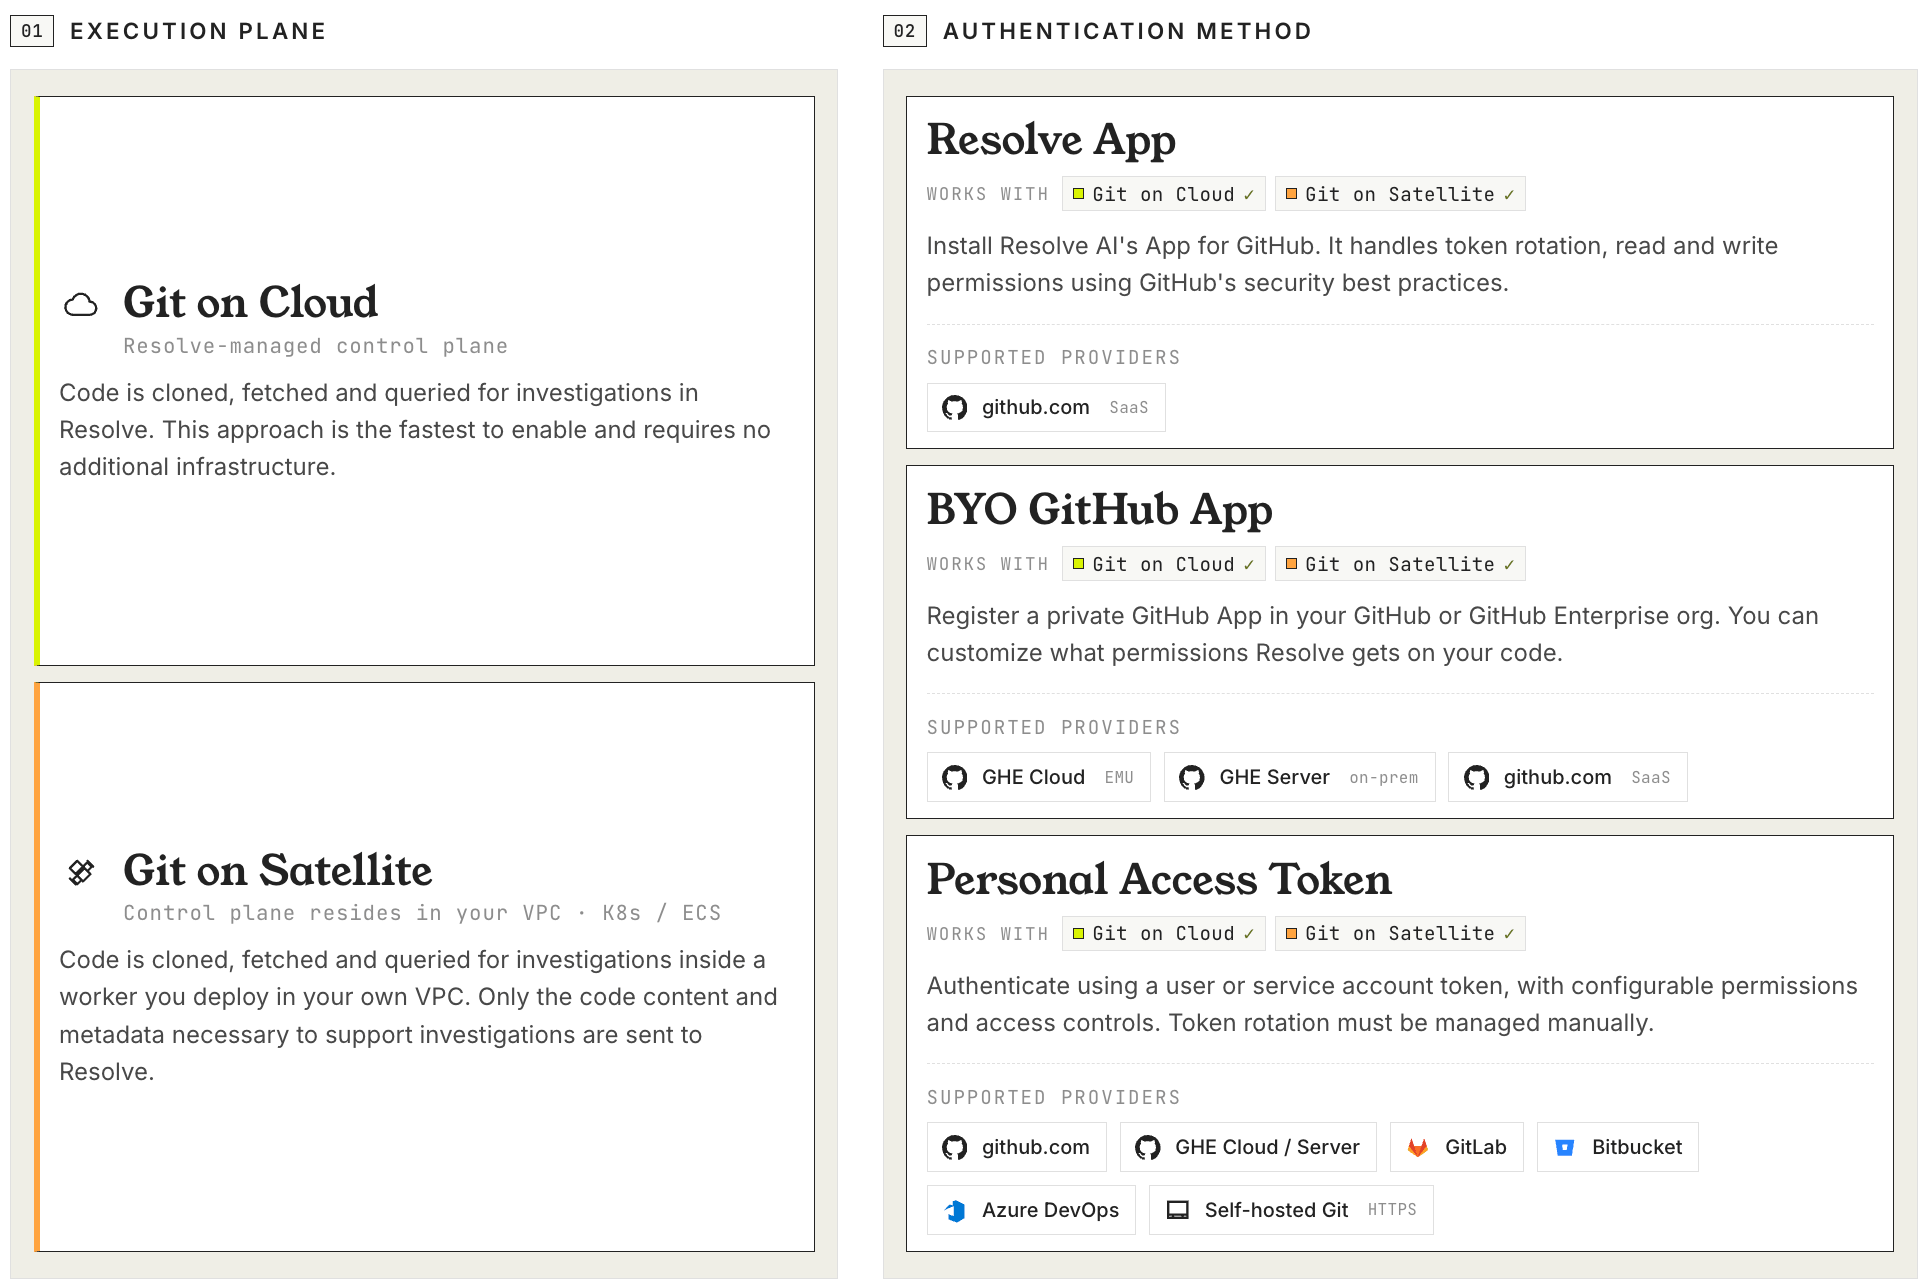
Connecting ResolveAI to your code comes down to two independent choices:- Where Git commands run: Git on Cloud (Resolve-managed) or Git on Satellite (your Kubernetes / ECS).
- How Resolve authenticates:
github(ResolveAI’s App for GitHub),ghe(Bring-Your-Own GitHub App), ortoken(PAT). All three work on both Cloud and Satellite.
1. Choosing an execution plane: Cloud or Satellite
Your first decision is where Resolve actually clones, fetches, and queries your repositories. The right choice depends on your network reachability, your data residency requirements, and how much infrastructure your team is prepared to operate.
The Resolve Satellite is supported on Kubernetes and on AWS ECS Fargate. The Kubernetes deployment stores repositories on a
gitVolume (PVC is recommended for production); the ECS deployment uses an EFS volume. Both are functionally identical, so the choice comes down to whichever infrastructure your team already operates.
Once you’ve decided, follow the matching setup guide:
- Set up Git on Cloud for Resolve-managed execution
- Set up Git on Satellite (Kubernetes) for in-cluster execution
- Set up Satellite on ECS for AWS Fargate execution
2. Choosing an authentication method
After picking an execution plane, decide how Resolve proves identity to your Git host. All three auth types work on both Cloud and Satellite — the choice is driven by which Git host your code lives on, your security policy, and how you want to manage the Git App.github— Connects to github.com through ResolveAI’s App for GitHub. You complete an OAuth-style installation, and Resolve handles token rotation automatically.ghe— Connects through a custom GitHub App that you own, on any GitHub variant (github.com, GitHub Enterprise Cloud, or GitHub Enterprise Server). You provide the App ID, installation ID, and private key, and Resolve calls the API base URL you configure.token— Connects to non-GitHub providers (GitLab, Bitbucket, Azure DevOps, self-hosted Git) or to GitHub via PAT. Resolve authenticates with the username and personal access token you provide.
One integration can use all three auth types: A single Git integration can carry multiple auth configs side-by-side under
authConfigs — for example, one github config for github.com repos, one ghe config for an on-prem GHE instance, and one or more token configs for GitLab or Bitbucket. Each is keyed independently and matched to its credentials.Match your setup to an auth type
Once you’ve decided, follow the matching walkthrough:
- Connect via ResolveAI’s App for GitHub for
githubauth on github.com - Bring Your Own GitHub App for
gheauth (github.com, GHE Cloud, or GHE Server) - For
tokenauth, first create the PAT, then complete the connection under Option 3 in the Cloud or Satellite guide
What Resolve can do once connected: reads vs writes
These behaviors apply to both Cloud and Satellite:- Reads are always enabled. Cloning, fetching, searching, reading files, viewing history, generating diffs, and inspecting blame data.
- Write/remediation tools (proposing code changes, opening PRs) are controlled by
disableWrites:- With a
githuborgheauth config, writes are enabled by default. - With token-only auth, writes are disabled by default.
- Set
disableWritesexplicitly in your connection config to override either default.
- With a
authConfigs, tokenAuthCredentials, gheAuthCredentials, disabledSubcommands, certificate overrides), see the Git on Cloud or Git on Satellite setup guide.
Creating access tokens
When you usetoken auth, you provide a username and personal access token (PAT) that Resolve uses to authenticate to your Git host. The steps below apply to every execution plane. Create the token here, then follow your setup guide (Cloud, Satellite, or ECS) for where to store it.
Every token can be created in one of two flavours, regardless of provider:
- Write (remediation), recommended: Resolve investigates and also proposes fixes, pushing a branch and opening a pull/merge request for your review. Requires write scopes on the token and
disableWrites: falseon the connection. - Read-only (restricted): Resolve clones code and reads commits, branches, pull/merge requests, pipelines/CI, and metadata, but cannot open PRs/MRs. This is the technical default for token-only auth (
disableWrites: true). Choose it only if your policy requires investigate-only access.
GitHub
GitHub supports fine-grained and classic PATs.Fine-grained token (recommended)
Fine-grained token (recommended)
- Go to Settings > Developer settings > Personal access tokens > Fine-grained tokens.
- Click Generate new token and set a name and expiration.
- Choose the resource owner and select the repositories to grant access to.
- Set repository permissions:
- Read and write on Contents (code) and Pull requests. These two enable pull-request creation. Set them to Read-only if you only need investigation reads.
- Read-only on Metadata (mandatory), Actions, Checks, Commit statuses, Deployments, Discussions, Issues, and Merge queues.
- If your org uses SSO, authorize the token for SSO after creation.
- Generate and copy the token.
Classic token
Classic token
- Go to Settings > Developer settings > Personal access tokens > Tokens (classic).
- Generate a token and set an expiration.
- Select scopes:
- Private repositories:
repo. - Public-only workflows:
public_repo.
- Private repositories:
- Authorize SSO for your org if required.
- Copy the token.
GitLab
GitLab access is gated by two independent controls, and you must satisfy both:- Token scopes: the checkboxes you select when creating the PAT.
- Membership role: the role (Guest, Reporter, Developer, and so on) the token’s owner has on the projects or groups you connect.
api-scoped token owned by a Reporter still cannot push or open merge requests. Pick the flavour that matches what you want Resolve to do.
Merge-request creation (write, recommended)
Merge-request creation (write, recommended)
Lets Resolve investigate and open merge requests for your review. Includes every read capability, plus branch push and MR creation.
- Go to Preferences > Access Tokens (or use a project/group access token).
- Create a token with an expiration.
-
Select scope:
api: the only read-write API scope. It covers MR creation and also includes Git-over-HTTPS clone/fetch/push, so it subsumesread_repository/write_repository.
write_repositoryis not sufficient on its own. It only enables Git push over HTTPS and does not support API authentication, so it cannot create a merge request. - Ensure the owner has at least the Developer role on the connected projects/groups. Developer is the minimum role that can push branches and create merge requests.
- Copy the token.
disableWrites: false on the connection to allow write/remediation tools.Read-only (restricted)
Read-only (restricted)
Lets Resolve clone code and read commits, branches, merge requests, pipelines, CI job logs, and project metadata, but not open merge requests. Choose this only if your policy requires investigate-only access.
- Go to Preferences > Access Tokens (for a personal token), or use a project/group access token to scope it to specific repos.
- Create a token with an expiration.
-
Select scopes:
read_repository: clone/fetch code over HTTPS.read_api: read merge requests, pipelines, jobs, commits, and metadata via the GitLab API.
read_repositoryalone does not grant API reads of MRs/pipelines, andread_apialone does not grant Git-over-HTTPS clone. - Ensure the owner has at least the Reporter role on the connected projects/groups. On private projects, Guest cannot read code, so Reporter is the minimum.
- Copy the token.
disableWrites: true (the default for token-only auth) for this flavour.Classic GitLab PATs are not per-repository like GitHub fine-grained tokens. They can access every project the owning user can. To limit blast radius, use a project or group access token (assign it the Reporter or Developer role per the flavour above) or a fine-grained personal access token instead of a classic PAT.
Other providers (Bitbucket, Azure DevOps, self-hosted)
Token auth works with any provider that supports HTTPS PATs. The principle is the same as above: grant the minimum the flavour needs.- Read-only: scopes that allow repository read/clone plus reading pull requests and pipelines/builds (e.g. Bitbucket Repositories: Read + Pull requests: Read + Pipelines: Read; Azure DevOps Code (Read) + Build (Read)).
- Write (remediation): add the provider’s repository-write and pull-request-write scopes so Resolve can push branches and open PRs.