This setup must be completed by an Azure AD Administrator.
1. Create a Custom SAML App
- Go to your Azure Portal
- Navigate to Azure Services -> Enterprise applications
- Click + New application
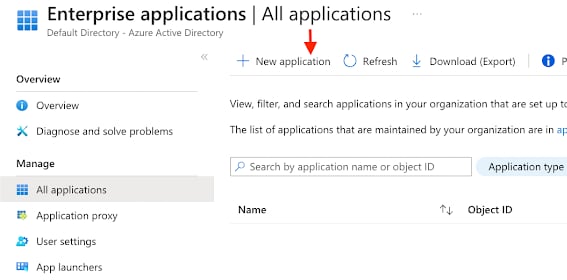
- Click + Create your own application
- Name the app
ResolveAI - Select Integrate any other application you don’t find in the gallery
- Click Create
- Download the ResolveAI logo and add it as the icon
- Click Next to continue
2. Configure Single Sign-On (SAML)
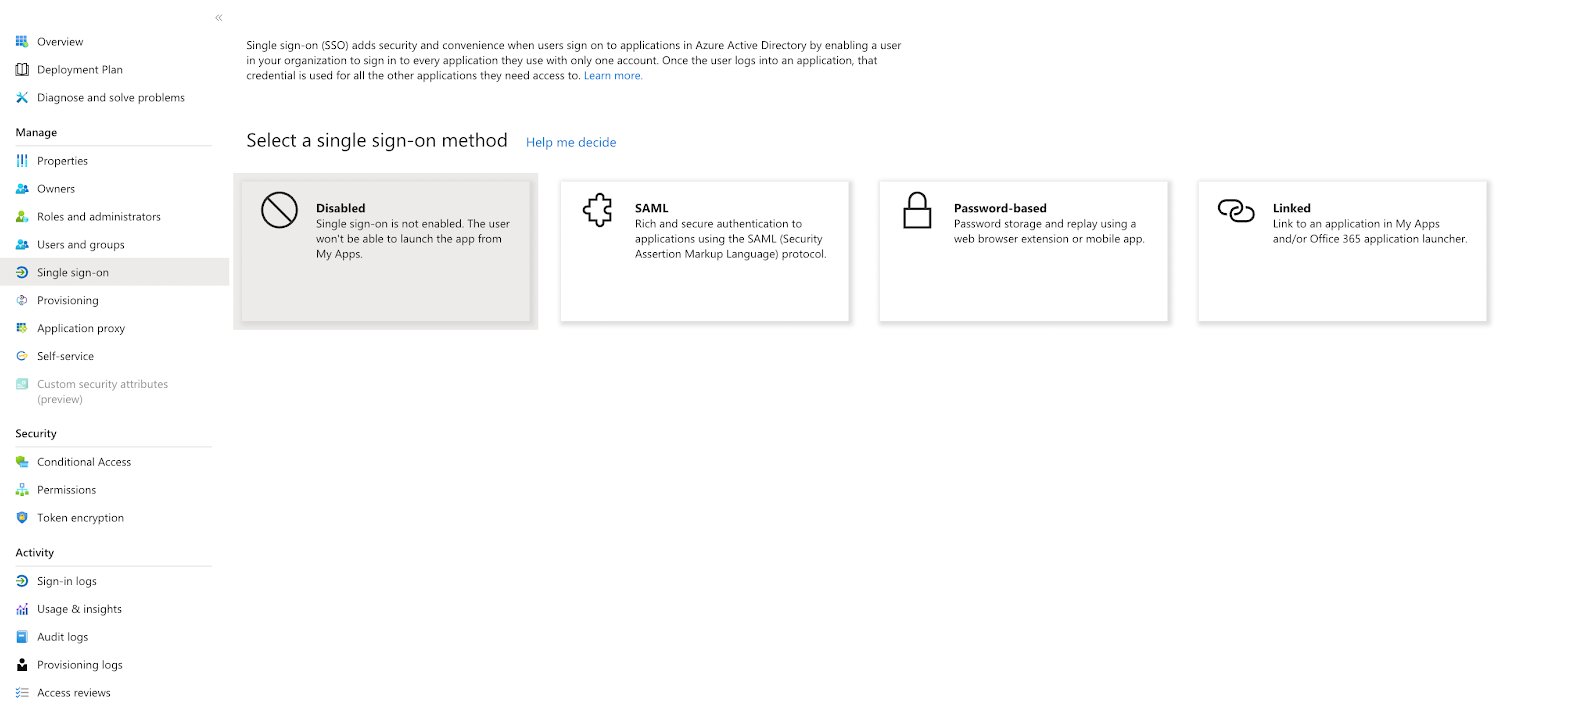
- From the app’s Overview page, click Single sign-on
- Choose the SAML sign-on method
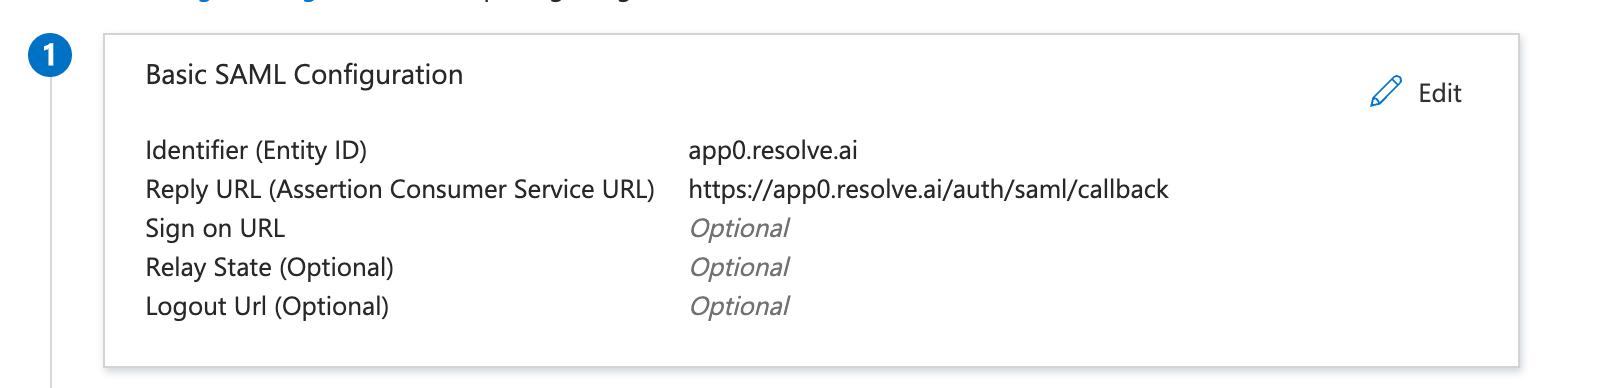
Basic SAML Configuration
- Identifier (Entity ID):
app0.resolve.ai - Reply URL (ACS URL):
https://app0.resolve.ai/auth/saml/callback - Relay State: leave blank
3. Configure Attributes & Claims
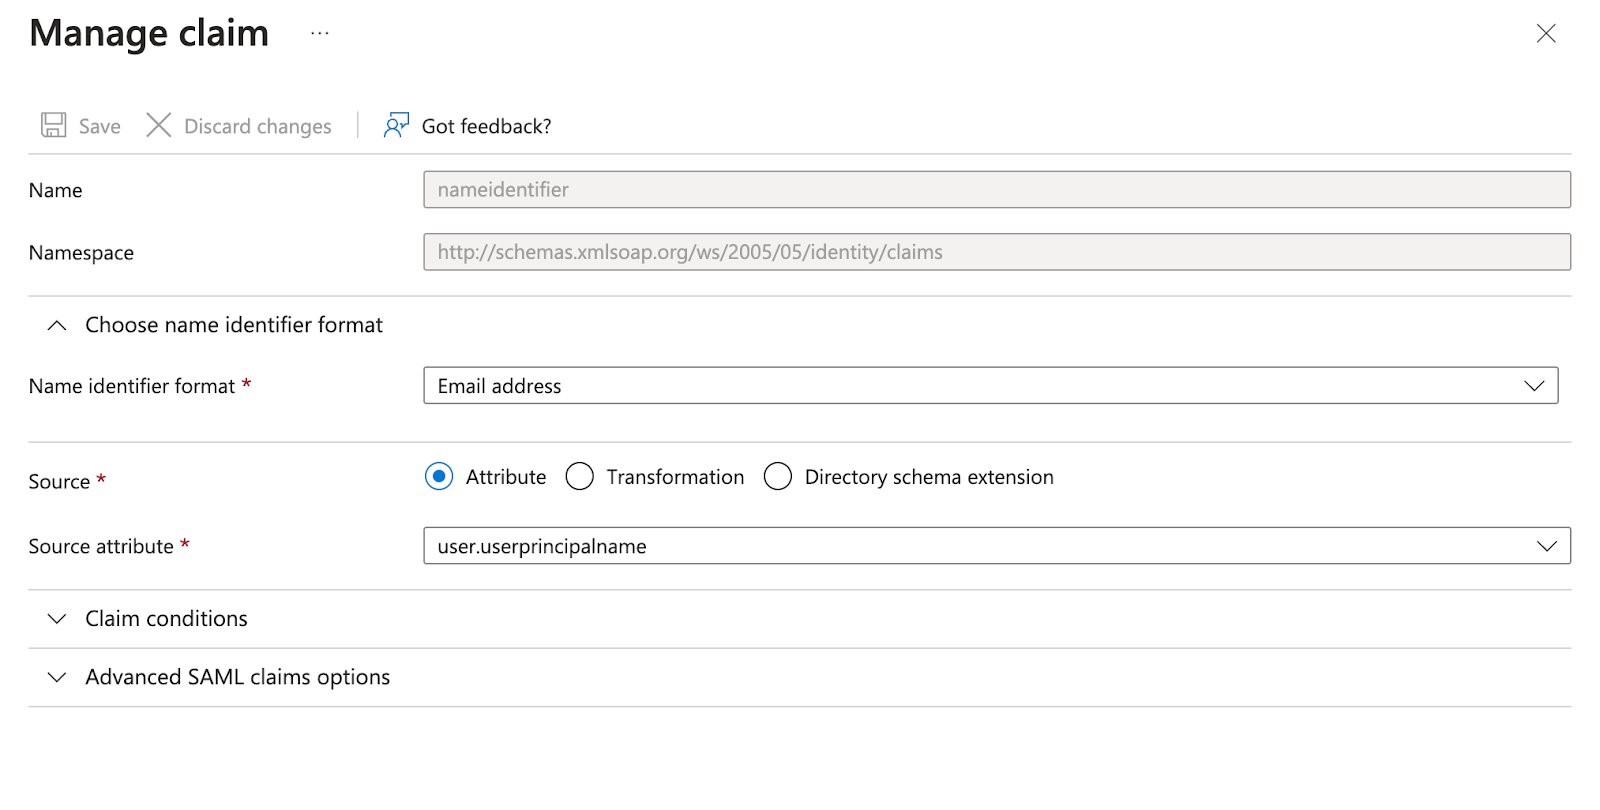
In the User Attributes & Claims section, configure the following:- nameidentifier:
user.userprincipalname
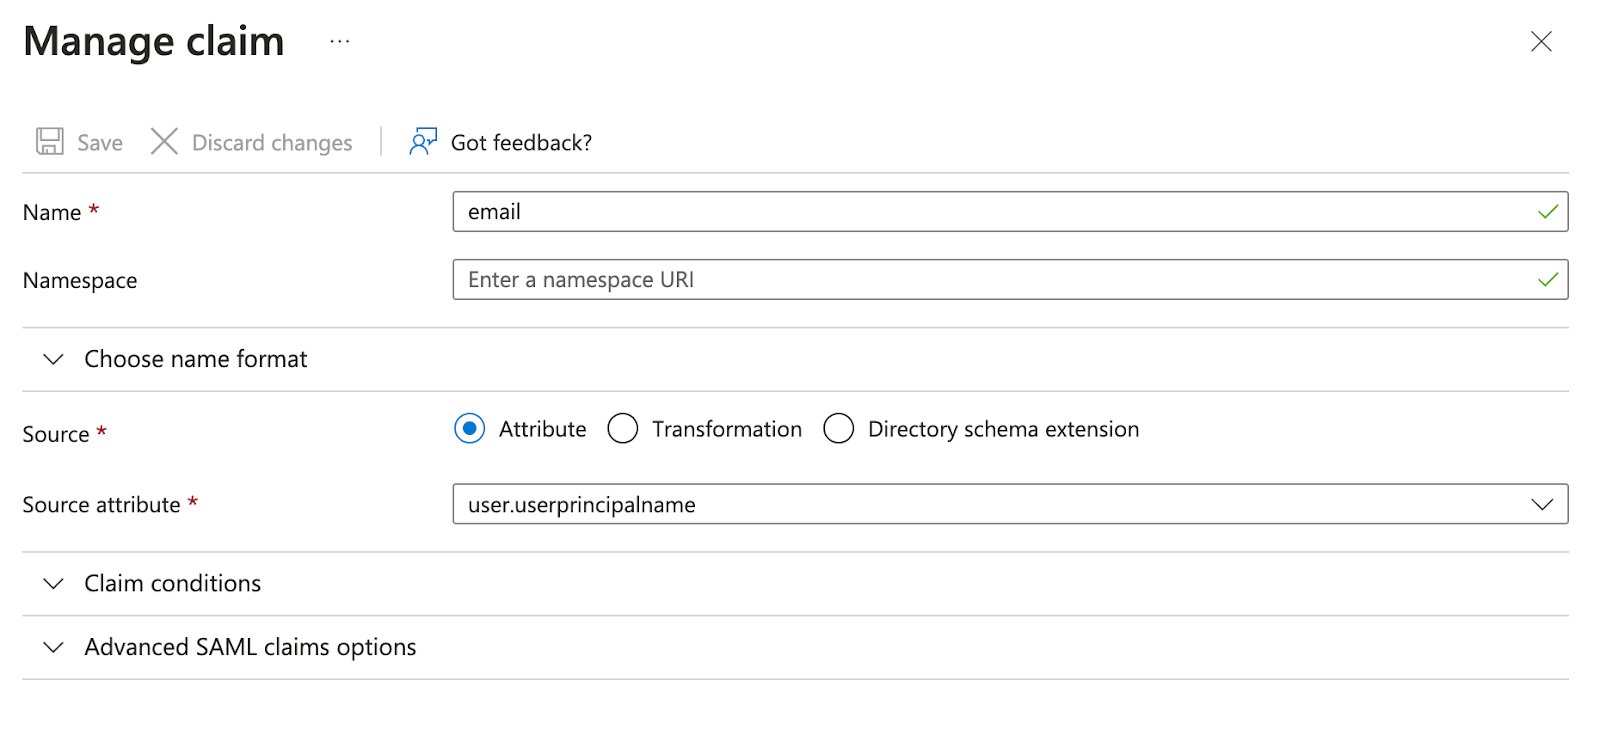
- email:
user.userprincipalnameoruser.mail
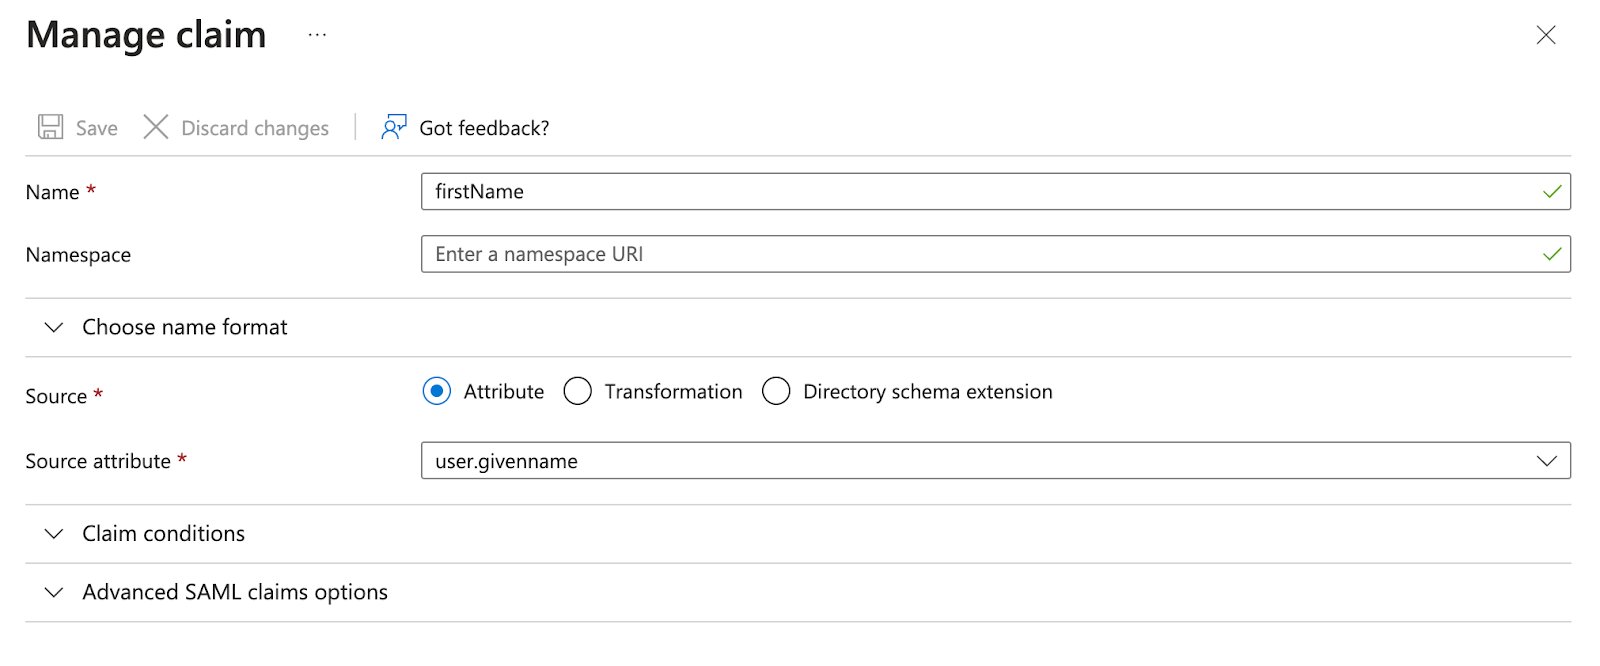
- firstName:
user.givenname
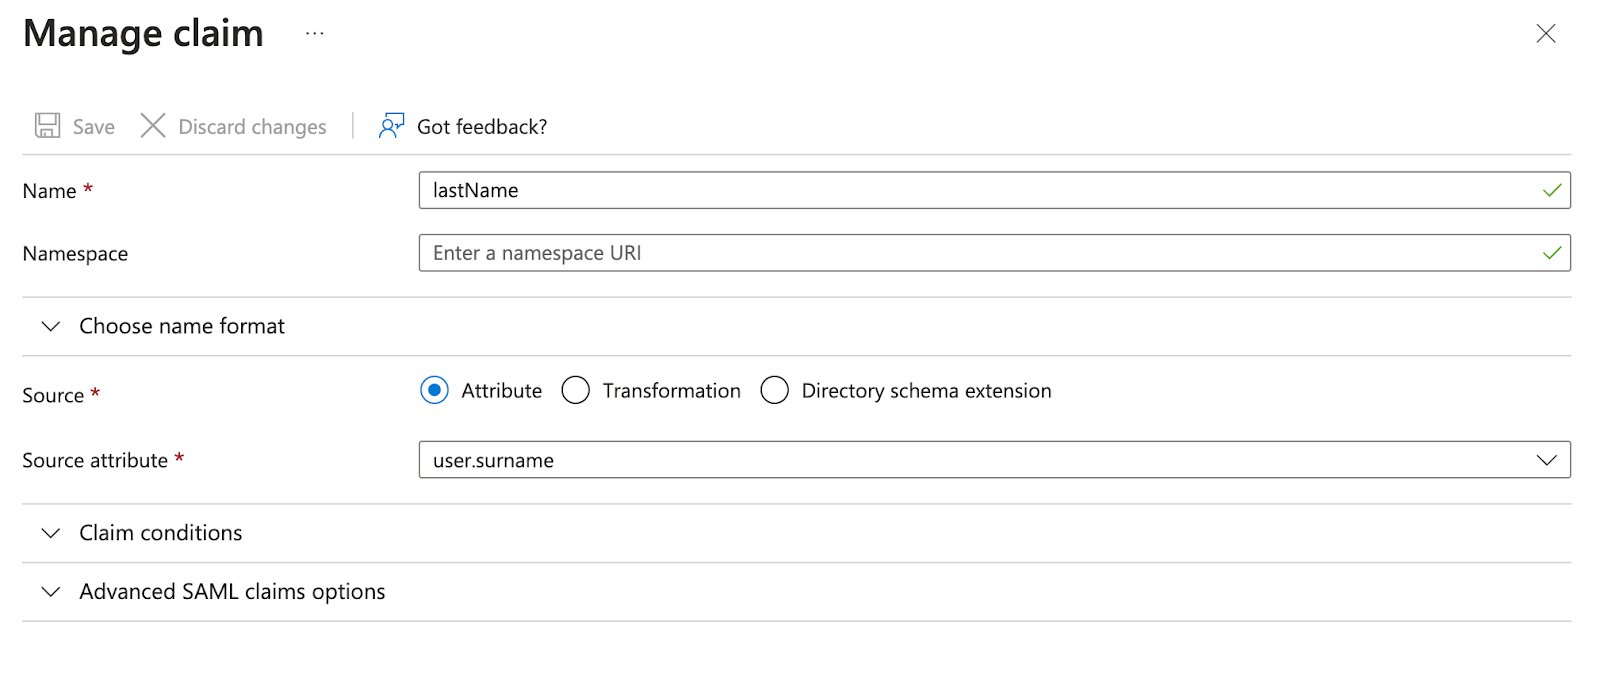
- lastName:
user.surname
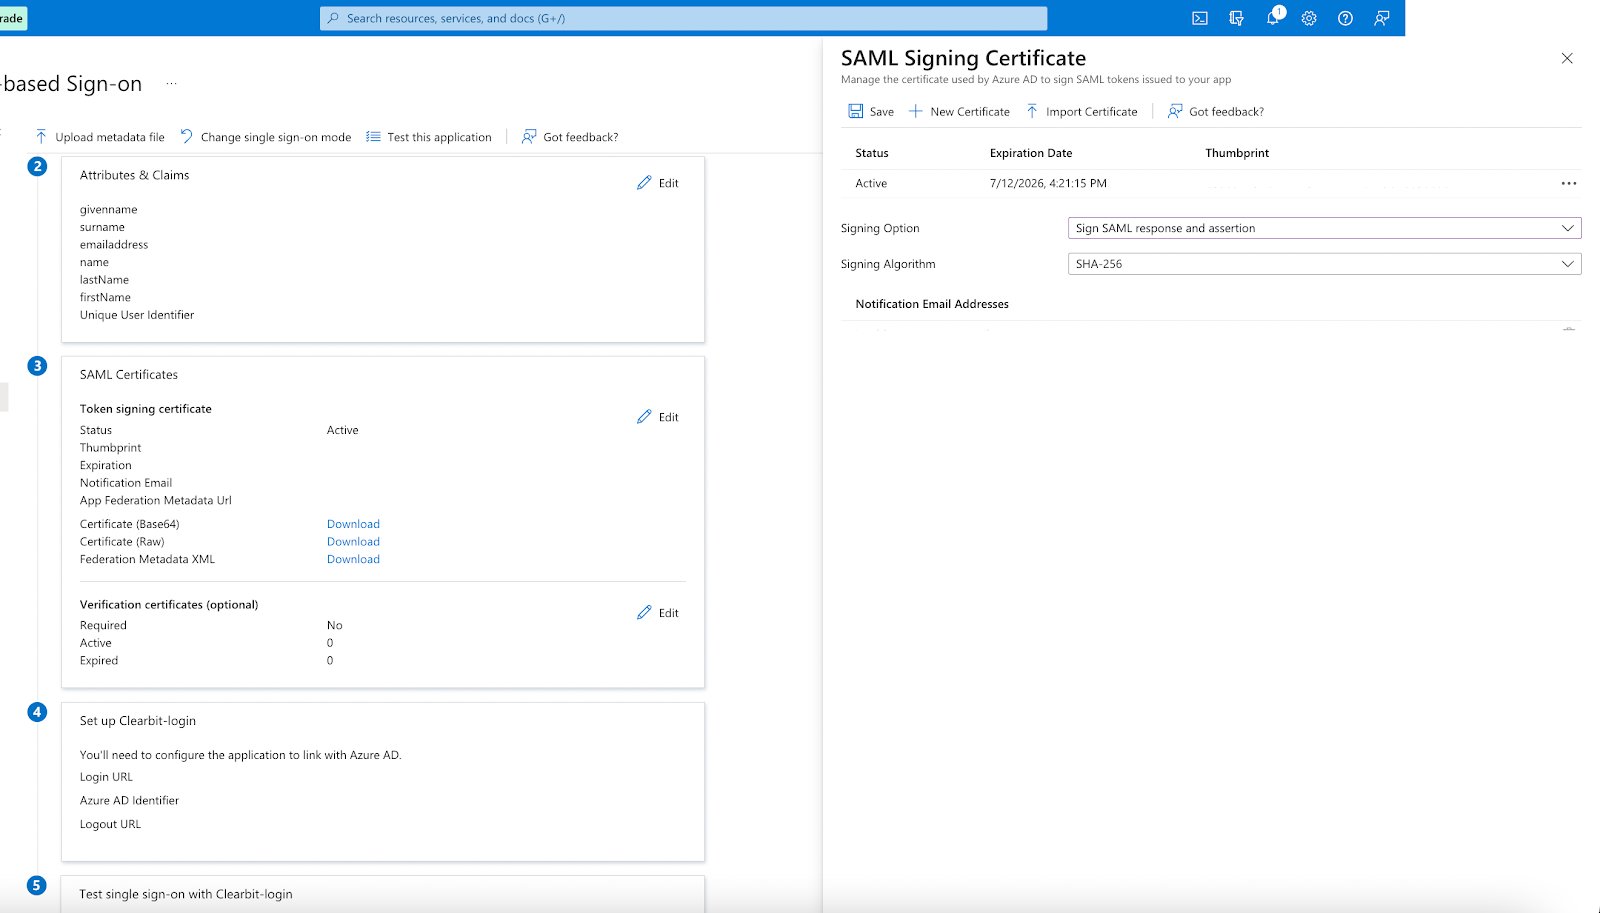
4. Assign Users and Groups
Assign the app to users or groups who need access to Resolve. Only those assigned can authenticate. To learn more: Assign users and groups in Azure5. Contact ResolveAI
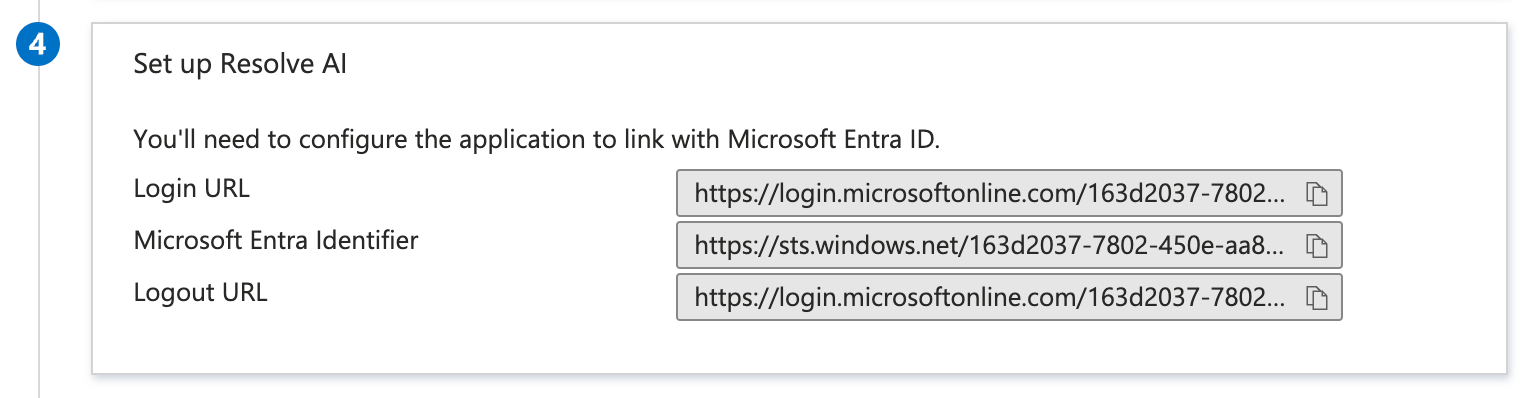
After setup, copy the following to share with your Resolve contact:- Login URL
- Logout URL
- Azure AD Identifier
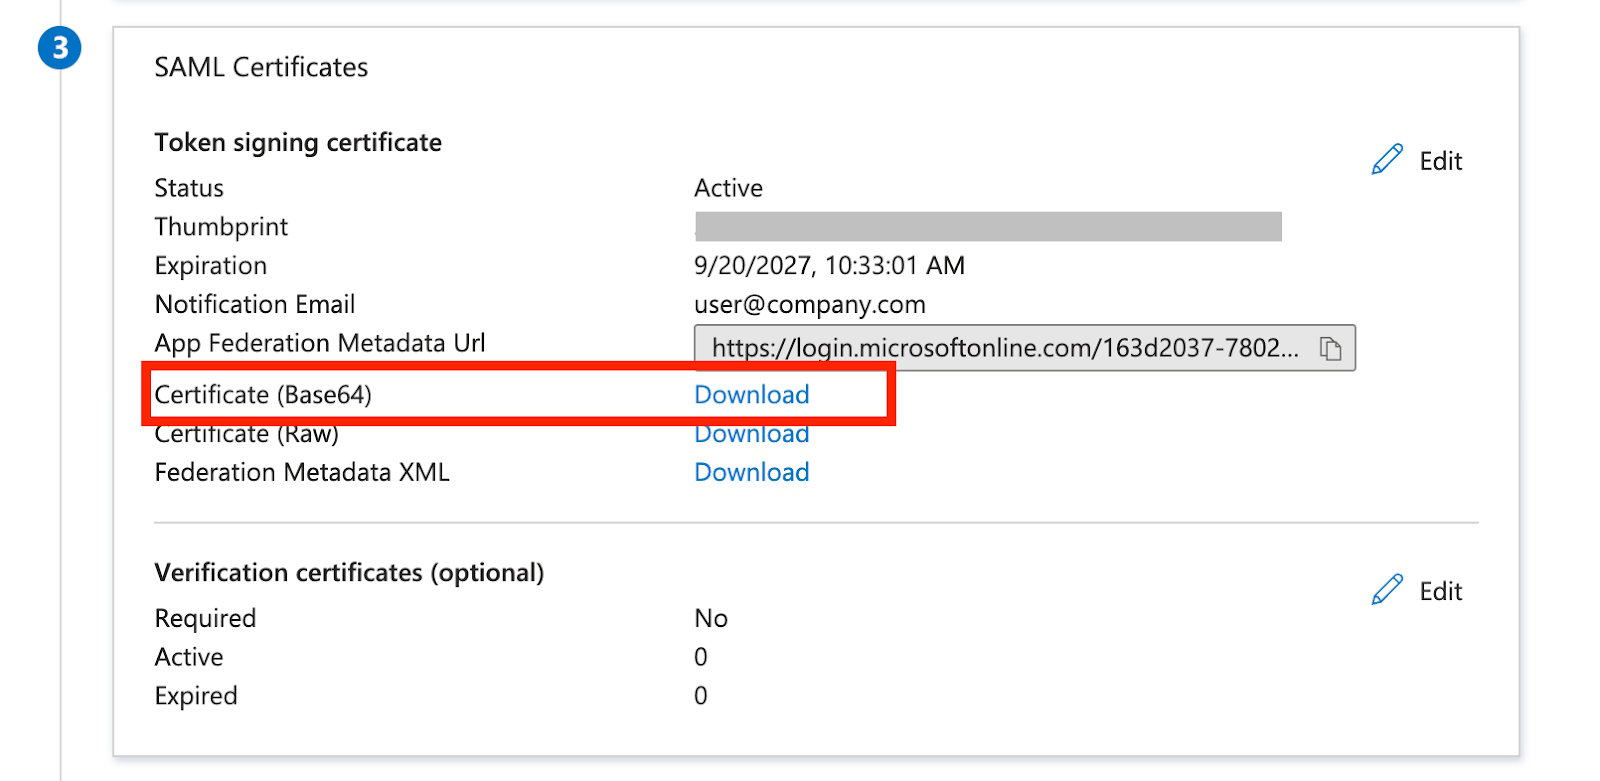
- Base64 Certificate